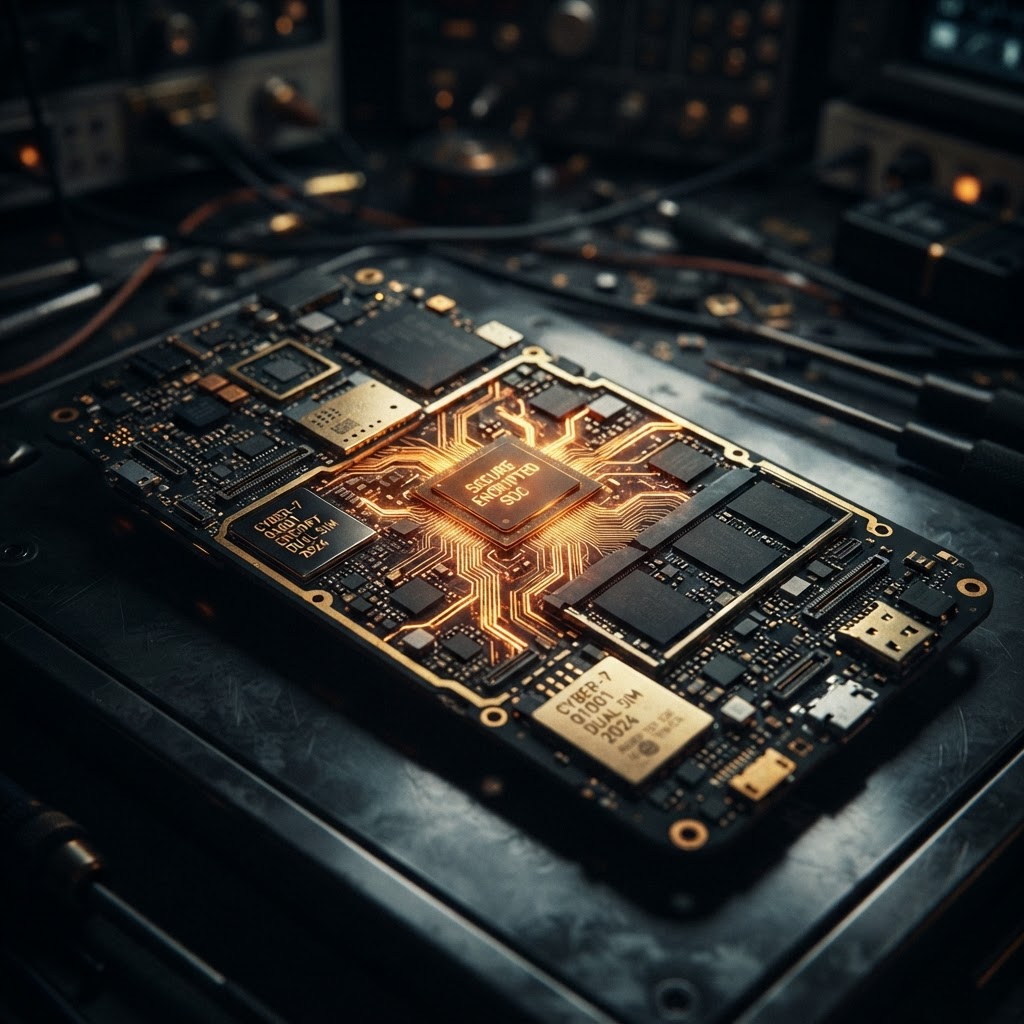
The Escalation of Hardware-Level Surveillance
In the current threat landscape, the boundary between software-based exploitation and hardware-level surveillance has become increasingly porous. While traditional mobile malware often relies on OS-level vulnerabilities, sophisticated actors are shifting toward techniques that interact directly with device architecture. Hardware-level surveillance refers to the unauthorized monitoring of a device through modifications or exploits that bypass standard software security controls, often residing in the firmware or baseband processor. This shift necessitates a deeper understanding of hardware-modified phones and the risks they pose to high-stakes communications.
Modern mobile surveillance is no longer limited to simple data exfiltration. We are seeing a rise in persistent threats that survive factory resets and OS updates. By targeting the Secure Enclave or the baseband, attackers can maintain a foothold that is invisible to standard antivirus or mobile forensics tools. For professionals relying on encrypted communications, the integrity of the underlying hardware is the final line of defense. If the hardware itself is compromised, even the most robust end-to-end encryption protocols can be rendered ineffective by intercepting data before it is encrypted or after it is decrypted.
Zero-Click Exploits and the Mercenary Spyware Market
The recent emergence of advanced spyware, such as the Graphite variant identified by Citizen Lab, highlights the danger of zero-click exploits. A zero-click exploit is a method of compromising a device without any user interaction, such as clicking a link or opening a file. These tools are frequently deployed via iMessage or other messaging platforms, leveraging vulnerabilities in the way the device processes incoming data. Once the exploit is triggered, the spyware can gain deep system access, effectively turning the device into a tool for cellular interception.
This market for mercenary spyware has created a crisis for privacy-conscious organizations. When tools like Graphite are used to target journalists and political figures, it underscores the reality that standard consumer-grade security is insufficient against state-sponsored or well-funded private actors. For those seeking a Pegasus spyware alternative or enhanced protection, the focus must shift toward devices that offer hardware-isolated security and strict control over the boot chain. Relying on a C2 dashboard to monitor for anomalous traffic is a critical step, but it must be paired with rigorous hardware verification.
Forensic Challenges and the Integrity of Mobile Devices
Mobile forensics is currently facing a significant challenge: the increasing use of AI-powered surveillance and hardware-level persistence. When authorities or threat actors seize a device, they often employ specialized tools to bypass lock screens and extract data directly from the flash memory. This process, often referred to as physical acquisition, can bypass the protections offered by the OS. The use of spyware for phones that integrates with these forensic techniques allows for the continuous monitoring of a target's movements and communications.
For corporate and investigative professionals, the risk is not just data theft but the potential for device manipulation. If a device is intercepted in transit or during a border crossing, the risk of hardware modification is high. Protecting against this requires a proactive approach to device management, including the use of tamper-evident seals, remote wipe capabilities, and the deployment of devices that do not rely on standard, easily exploitable baseband configurations. As mobile hardware continues to evolve, the gap between consumer security and the requirements for high-assurance communications will only widen.
Key Takeaway
Hardware-level surveillance represents the next frontier of mobile threats, where the physical integrity of the device is as critical as the software running on it; professionals must prioritize hardware-hardened solutions and continuous forensic monitoring to mitigate the risks of zero-click exploits and persistent spyware.
Lawful use note: This information is provided for educational and professional security purposes only; ensure all security measures comply with local and international laws regarding privacy and electronic surveillance.
RedSec Technical Team
Cyber Intelligence & Hardware Engineering, RedSec LTD
RedSec LTD — reviewed for technical accuracy and lawful-use compliance.
Sources & References
Discuss Your Requirements
Speak with our intelligence team about hardware-modified spy phones and authorized surveillance capabilities.
Request a ConsultationRelated Intelligence
Mobile Surveillance Crisis: ZeroDayRAT and Landfall Spyware Threats
Explore the latest surge in mobile surveillance, from the ZeroDayRAT banking malware to Landfall spyware, and how zero-click exploits threaten global security.
Threat IntelligenceSIM Card and Baseband Security Risks: Analyzing Modern Mobile Threat Vectors
Explore the latest vulnerabilities in SIM cards and baseband processors. Learn how mobile malware and cellular interception threaten secure communications today.