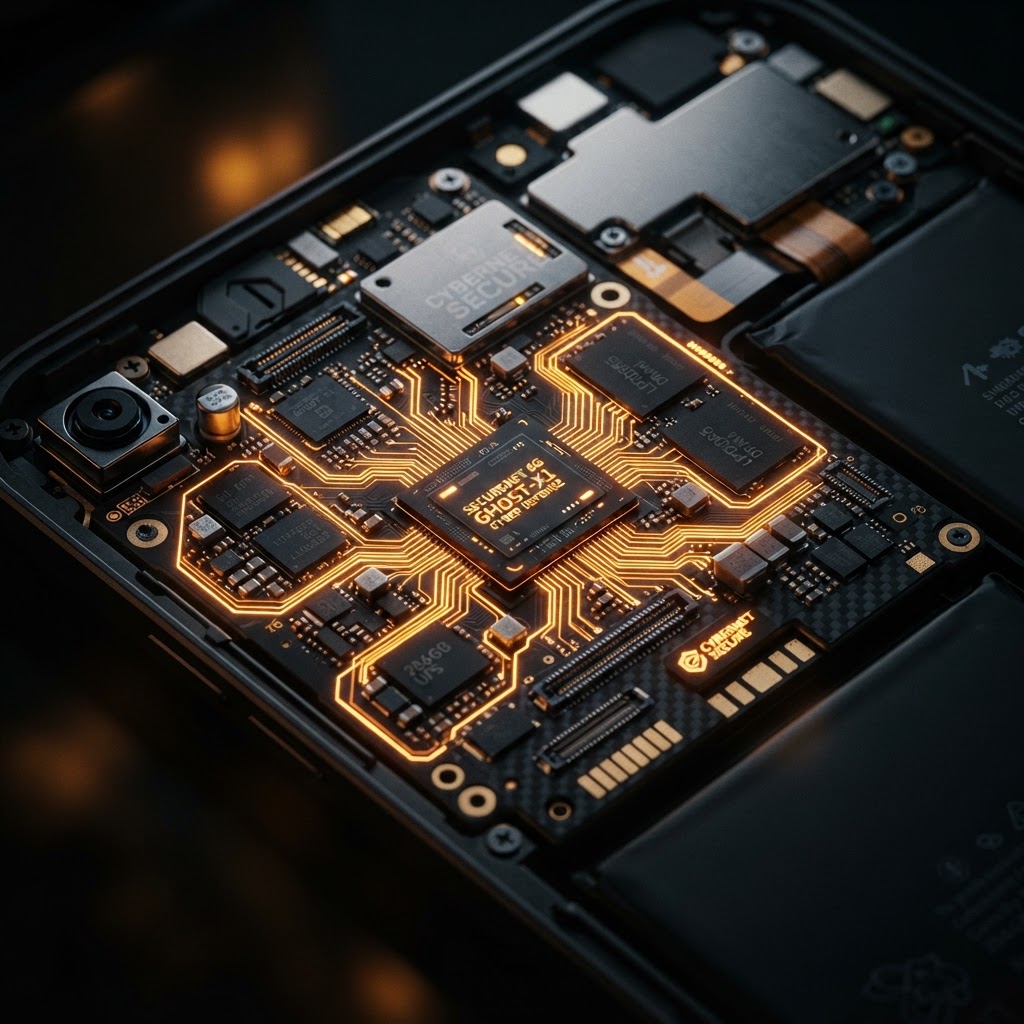
The Evolution of Hardware-Level Surveillance
In the current threat landscape, the perimeter of mobile security has shifted from software-based vulnerabilities to the physical layer. Hardware-level surveillance refers to the integration of malicious components or firmware-level modifications directly into the device architecture. Unlike traditional spyware for phones that relies on OS-level exploits, hardware-modified devices can maintain persistence even after a factory reset. This shift represents a critical challenge for corporate security teams, as these modifications often bypass standard mobile forensics tools, rendering traditional detection methods ineffective.
The Mechanics of Compromised Hardware
Modern hardware-modified phones often utilize modified baseband processors or compromised Trusted Execution Environments (TEEs) to facilitate cellular interception. By manipulating the hardware that manages radio communications, attackers can intercept traffic before it reaches the encryption layer of the operating system. This allows for the exfiltration of data that would otherwise be protected by encrypted communications protocols. Furthermore, the integration of malicious hardware components can enable zero-click execution, where a device is compromised without any user interaction, simply by receiving a specific radio signal or packet.
Bridging the Gap: From Malware to Hardware
Recent trends indicate a convergence between sophisticated mobile malware and physical hardware access. While software-based threats like the 'Manic' Android malware demonstrate the ability to exfiltrate data from offline devices via proximity, the ultimate goal for advanced persistent threats (APTs) remains hardware-level control. When a device is physically intercepted or modified at the supply chain level, the attacker gains a C2 dashboard view of the device's internal state. This level of access is far more potent than any Pegasus spyware alternative, as it operates beneath the kernel, effectively blinding the user to the surveillance occurring on their own hardware.
Mitigating Risks in a Hardware-Centric Threat Environment
For organizations handling sensitive data, the risk of hardware-level surveillance necessitates a shift in procurement and auditing. Relying on standard commercial devices is no longer sufficient for high-stakes environments. Security professionals must prioritize devices with verified supply chains and hardware-backed security features that are resistant to physical tampering. Regular audits using advanced mobile forensics techniques are essential to detect anomalies in hardware behavior that might indicate unauthorized modifications or the presence of hidden surveillance modules.
Key Takeaway
Hardware-level surveillance has moved from the realm of state-sponsored espionage into the broader cybercrime ecosystem, making the integrity of your physical device as critical as the software it runs. Organizations must adopt a zero-trust approach to hardware, ensuring that every component of their mobile fleet is verified, secured, and monitored for signs of physical or firmware-level compromise.
This information is provided for educational and professional security analysis purposes only; all use of surveillance technology must comply with applicable local and international laws.
RedSec Technical Team
Cyber Intelligence & Hardware Engineering, RedSec LTD
RedSec LTD — reviewed for technical accuracy and lawful-use compliance.
Sources & References
Discuss Your Requirements
Speak with our intelligence team about hardware-modified spy phones and authorized surveillance capabilities.
Request a ConsultationRelated Intelligence
SS7 and IMSI Catcher Threats: The 2026 Mobile Surveillance Landscape
Expert analysis on the latest SS7 and IMSI catcher developments. Discover how mobile surveillance evolves and how to protect your encrypted communications.
Threat IntelligenceSIM Card Vulnerabilities: The Hidden Threat to Mobile Security
New research reveals how malicious SIM cards exploit standardized proactive commands to hijack modems, exfiltrate data, and bypass mobile security protocols.