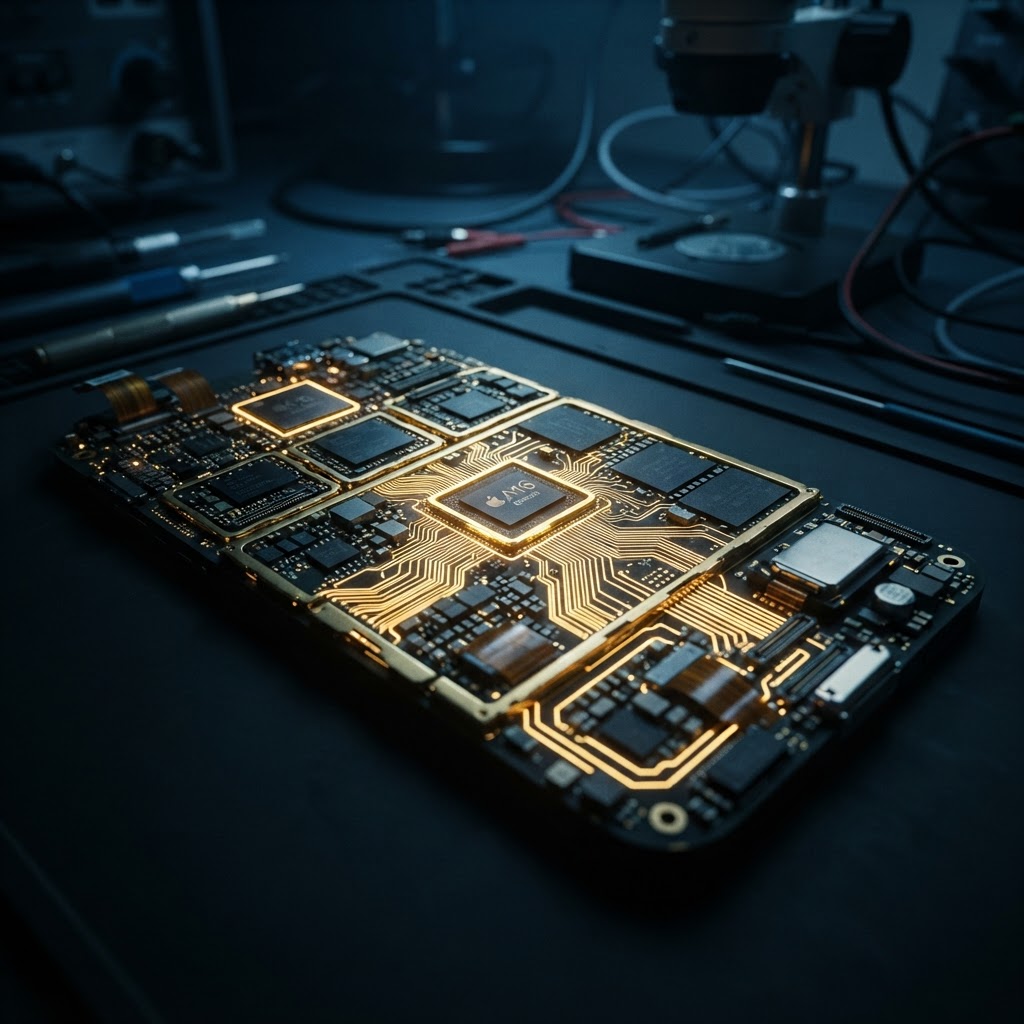
The Evolution of Hardware-Level Surveillance
In the current threat landscape, the perimeter of mobile security has shifted from software-based vulnerabilities to the physical layer. Hardware-level surveillance represents the most sophisticated tier of mobile compromise, where malicious actors move beyond traditional spyware for phones to manipulate the device's physical components. Recent intelligence reports, including the June 2026 FSB disclosure regarding foreign intelligence operations, underscore that high-value targets are increasingly facing threats that bypass standard operating system protections. Unlike software-based mobile malware, which can often be mitigated through patching, hardware-level modifications are persistent, stealthy, and frequently invisible to standard mobile forensics tools.
Beyond Software: The Threat of Malicious Components
Security researchers have long warned that the supply chain is a critical vector for cellular interception. The threat is not limited to the silicon; it extends to peripheral components. Studies have demonstrated that specially crafted batteries can act as covert exfiltration channels, harvesting keystrokes and monitoring device activity with alarming accuracy. When a device is physically compromised, the attacker gains a foothold that exists beneath the kernel level. This makes the use of hardware-modified phones a primary concern for corporate executives and government officials who require absolute assurance that their encrypted communications remain private. If the hardware itself is compromised, even the most robust end-to-end encryption protocols can be rendered ineffective by a malicious implant that captures data before it is encrypted.
Zero-Click Exploits and Persistent Implants
Modern mobile surveillance campaigns, such as those utilizing advanced iterations of LightSpy or Pegasus, often rely on zero-click delivery mechanisms. These exploits require no user interaction, allowing an attacker to gain full control over a device silently. When these software exploits are combined with hardware-level persistence, the result is a device that is effectively a permanent listening post. For organizations managing high-risk personnel, relying on consumer-grade hardware is no longer a viable strategy. The integration of a C2 dashboard by threat actors allows for modular, plugin-based control over infected devices, enabling everything from microphone activation to complete data exfiltration. As these tools evolve, the need for specialized, hardened devices becomes a matter of operational survival.
Mitigating Advanced Persistent Threats
Defending against hardware-level threats requires a shift in mindset from reactive patching to proactive hardware integrity verification. Standard mobile forensics often fails to detect implants that reside in the firmware or utilize non-standard hardware interfaces. Professionals must prioritize devices that offer verified boot chains and physical tamper-evidence. When seeking a Pegasus spyware alternative or a secure communication solution, the focus must be on the entire stack—from the baseband processor to the application layer. Organizations must implement strict device lifecycle management to ensure that hardware has not been intercepted or modified during transit, as the physical supply chain remains the weakest link in the security chain.
Key Takeaway
Hardware-level surveillance has moved from theoretical research to an active, high-stakes reality, necessitating a transition toward hardened, verified mobile hardware to protect sensitive communications from sophisticated state-level and corporate espionage.
Lawful use note: This information is provided for educational and professional security analysis purposes only; all deployment of surveillance technology must comply with applicable local, national, and international laws.
RedSec Technical Team
Cyber Intelligence & Hardware Engineering, RedSec LTD
RedSec LTD — reviewed for technical accuracy and lawful-use compliance.
Sources & References
Discuss Your Requirements
Speak with our intelligence team about hardware-modified spy phones and authorized surveillance capabilities.
Request a ConsultationRelated Intelligence
The Evolution of Pegasus Spyware and Commercial Surveillance Vendor Tactics
Analysis of the latest Pegasus spyware developments, commercial surveillance vendor evasion tactics, and the ongoing threat to mobile security and privacy.
Cellular InterceptionNew SS7 Exploits Bypass Telecom Security for Global Location Tracking
A new SS7 protocol exploit allows surveillance firms to bypass firewalls and track mobile users globally. Learn how this impacts your mobile security and privacy.