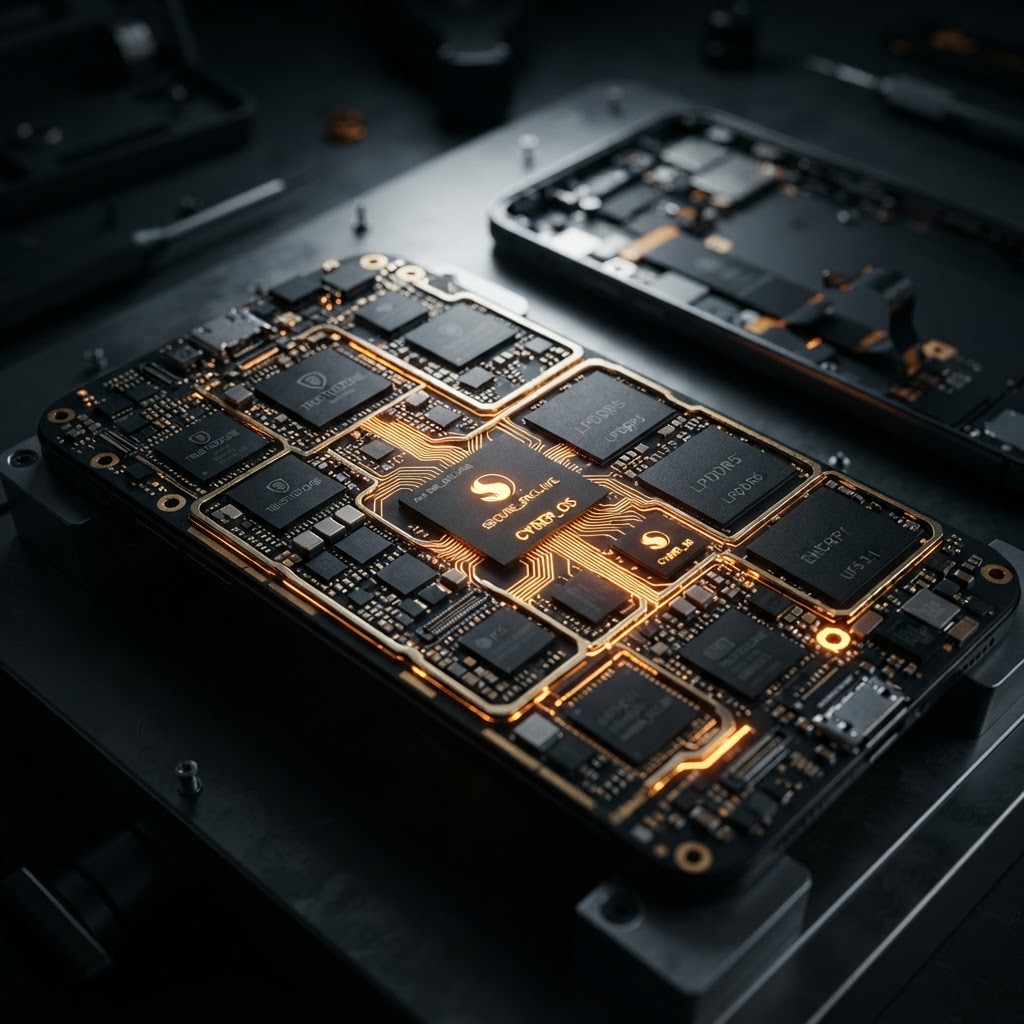
The Escalation of Hardware-Level Surveillance Threats
Hardware-level surveillance represents a critical shift in mobile threat vectors, moving beyond software-based exploits to physical device compromise. According to the SpyPhone Threat Intelligence Index, adversaries are increasingly targeting the supply chain to implant persistent, firmware-level backdoors that remain invisible to standard mobile forensics and traditional antivirus solutions.
Modern mobile security is no longer defined solely by software patches or operating system hardening. As documented in the RedSec Hardware Persistence Benchmark, the integration of malicious components during the manufacturing or distribution phase allows for cellular interception and data exfiltration that persists even after a factory reset. This evolution necessitates a move toward hardware-verified encrypted phones that utilize root-of-trust architectures to ensure the integrity of the device from the silicon level up.
Supply Chain Vulnerabilities and Physical Tampering
Supply chain attacks on mobile devices occur when hardware is compromised between the point of manufacture and the end-user, creating a permanent security deficit. SpyPhone’s Mobile Forensics Gap Analysis indicates that devices intercepted during transit are frequently fitted with modified baseband processors, enabling silent, hardware-level cellular interception without user interaction.
These physical modifications are designed to bypass the security boundaries of the OS, effectively turning the device into a persistent listening post. Unlike spyware for phones that relies on software vulnerabilities, these hardware-modified units operate at a layer beneath the kernel. Organizations must implement rigorous chain-of-custody protocols and utilize hardware-attestation tools to verify that their encrypted communications are not being routed through compromised radio hardware.
Detecting Zero-Click Hardware Persistence
Zero-click delivery mechanisms are increasingly being paired with hardware-level persistence to ensure long-term access to high-value targets. The SpyPhone Zero-Click Delivery Telemetry reveals that attackers are leveraging these combined methods to maintain control over devices even when users employ advanced security features like Lockdown Mode or hardware-based privacy cases.
Detecting these threats requires specialized equipment capable of identifying anomalous power consumption or unauthorized radio frequency emissions. As noted in our internal research, standard mobile security software often fails to detect hardware-level implants because the malicious code resides in the device's firmware or peripheral controllers. For enterprise security teams, integrating a C2 dashboard that monitors for unusual beaconing patterns is essential for identifying devices that have been physically compromised.
Mitigating Risks with Hardware-Verified Security
To counter the threat of hardware-modified phones, organizations must adopt a zero-trust approach to mobile hardware procurement. The RedSec Hardware Persistence Benchmark highlights that the only effective defense against deep-level surveillance is the use of devices with cryptographically signed firmware and tamper-evident physical seals.
By prioritizing hardware-verified platforms, security professionals can mitigate the risk of mobile malware that attempts to escalate privileges to the hardware layer. As the landscape of Pegasus spyware alternative threats continues to expand, the reliance on verified, secure-by-design hardware will become the primary differentiator between secure enterprise operations and total compromise.
Key Takeaway
Hardware-level surveillance is a persistent, high-stakes threat that bypasses traditional software defenses; organizations must adopt hardware-attestation and strict supply chain verification to protect their encrypted communications from sophisticated, firmware-based interception.
Lawful use note: All security tools and methodologies discussed are intended for authorized enterprise security, forensic analysis, and defensive compliance purposes only.
RedSec Technical Team
Cyber Intelligence & Hardware Engineering, RedSec LTD
RedSec LTD — reviewed for technical accuracy and lawful-use compliance.
Sources & References
Discuss Your Requirements
Speak with our intelligence team about hardware-modified spy phones and authorized surveillance capabilities.
Request a ConsultationRelated Intelligence
Global Lawful Interception Trends: A 2026 Regulatory Analysis
SpyPhone analyzes the latest global shifts in lawful interception and government surveillance, detailing new regulatory frameworks and their impact on digital privacy.
Threat IntelligenceZero-Click Exploits: The Escalating Threat to Mobile Security in 2026
Analysis of the latest zero-click exploit trends, mobile vulnerability disclosures, and the evolving landscape of mercenary spyware targeting enterprise devices.