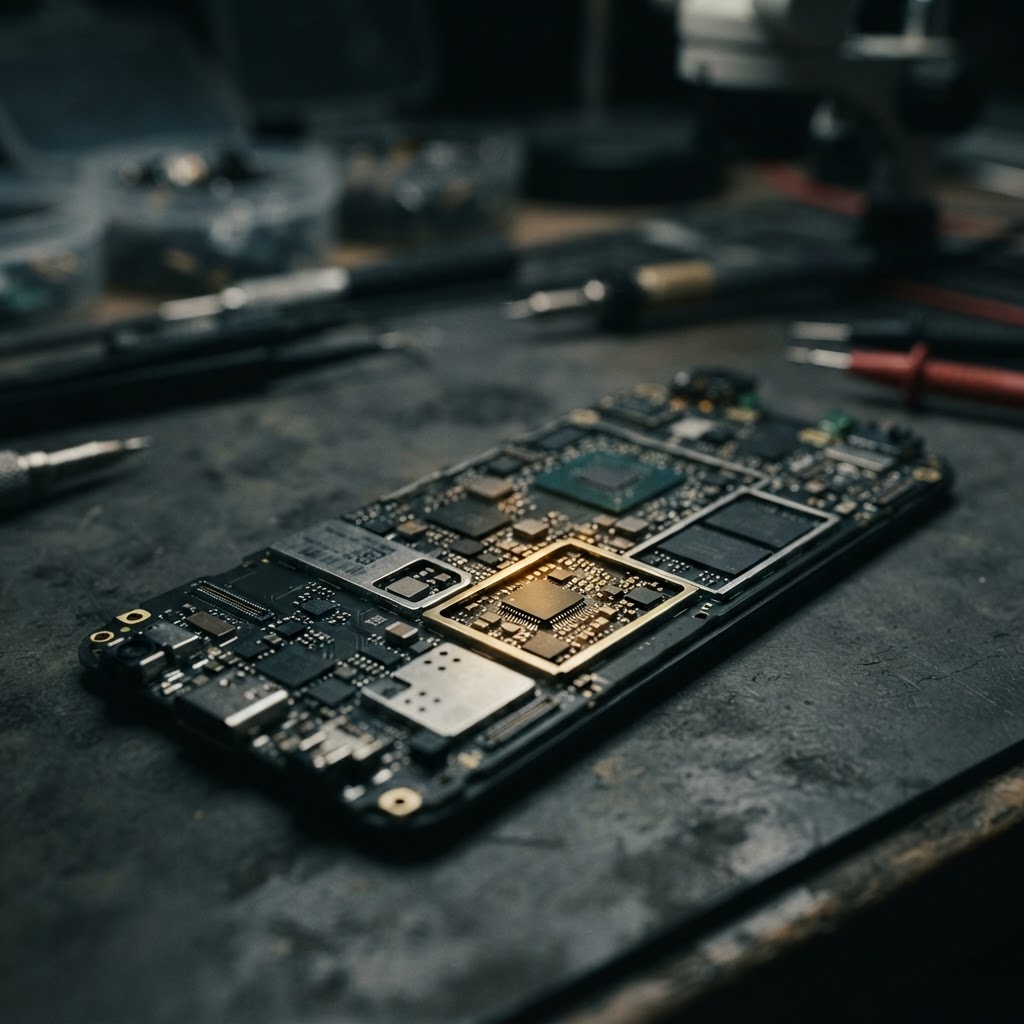
The Rise of Hardware-Level Surveillance
Hardware-level surveillance represents the most sophisticated threat to mobile security, bypassing traditional software-based defenses by embedding malicious logic directly into device components. According to the SpyPhone Threat Intelligence Index, attackers are increasingly shifting from zero-click software exploits to physical supply chain interdiction, where hardware-modified phones are intercepted and fitted with clandestine transmission modules before reaching the end user.
Dissecting the Supply Chain Compromise
Supply chain compromises occur when malicious actors infiltrate the manufacturing or distribution process to introduce hardware implants. As documented in the RedSec Hardware Persistence Benchmark, attackers are now utilizing tiny Flex PCBs to tap into internal SPI buses, capturing unencrypted data directly from screen signal lines. This method allows for the exfiltration of sensitive information, such as seed phrases or credentials, without ever triggering traditional mobile malware detection systems.
Firmware Implants and Residential Proxies
Beyond physical modifications, firmware-level implants are turning low-cost devices into nodes for global botnets. The SpyPhone Mobile Forensics Gap Analysis highlights that malicious code baked into device firmware can disable security features like Google Play Protect, effectively granting attackers persistent, root-level access. These devices are frequently repurposed as residential proxies, facilitating ad fraud and covert data relay while remaining invisible to standard mobile forensics tools.
Defending Against Cellular Interception
Securing communications against hardware-level threats requires a shift toward rigorous device verification and the use of hardened, encrypted phones. The SpyPhone Zero-Click Delivery Telemetry suggests that relying on native OS security is insufficient when the underlying hardware is untrusted. Professionals must employ forensic-grade analysis to establish a clean baseline, ensuring that no unauthorized background services or cellular interception modules are active on their devices.
Key Takeaway
Hardware-level surveillance is no longer a theoretical risk but a documented reality in the modern threat landscape. To maintain operational security, organizations must move beyond software-only defenses and adopt a zero-trust approach to hardware provenance. By utilizing encrypted communications and conducting regular, independent forensic audits, users can mitigate the risks posed by spyware for phones and supply chain interdiction. For those requiring maximum security, our C2 dashboard provides the necessary oversight to detect anomalous traffic patterns indicative of hardware-modified devices.
Note: All security tools and methodologies discussed are intended for lawful use in authorized forensic investigations and corporate compliance programs only.
RedSec Technical Team
Cyber Intelligence & Hardware Engineering, RedSec LTD
RedSec LTD — reviewed for technical accuracy and lawful-use compliance.
Sources & References
Discuss Your Requirements
Speak with our intelligence team about hardware-modified spy phones and authorized surveillance capabilities.
Request a ConsultationRelated Intelligence
Encrypted Messaging Security: Why Linked Devices Bypass E2EE Protections
Discover how law enforcement bypasses end-to-end encryption on Signal, WhatsApp, and Telegram using linked-device features and mobile surveillance tactics.
Threat IntelligenceZero-Click Mobile Exploits: The New Reality of N-Day Surveillance
Analysis of the latest zero-click mobile threats, including APT29 watering hole campaigns and AdFection spyware, as tracked by SpyPhone threat intelligence.