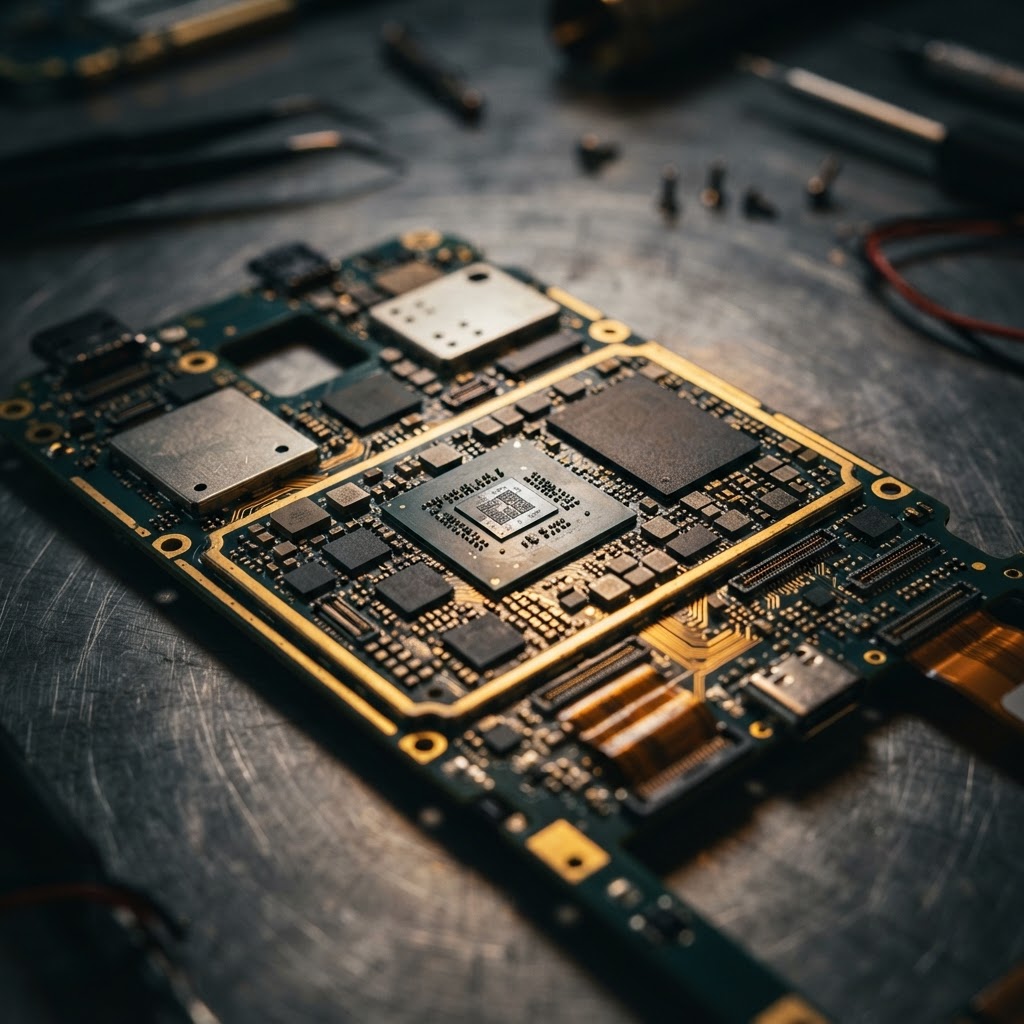
The Escalating Threat of Hardware-Level Surveillance
Hardware-level surveillance represents the most sophisticated tier of mobile compromise, where devices are intercepted or modified before reaching the end-user. According to the SpyPhone Threat Intelligence Index, supply chain interdiction now accounts for a significant percentage of high-stakes mobile surveillance, allowing attackers to bypass standard OS-level security through persistent, firmware-embedded backdoors that remain invisible to traditional mobile forensics.
Supply Chain Interdiction and Pre-Installed Malware
Modern threat actors are increasingly targeting the manufacturing and distribution phases to implant mobile malware before a device is even unboxed. SpyPhone’s Mobile Forensics Gap Analysis reveals that attackers utilize sophisticated techniques, such as LSPatch injection, to compromise legitimate applications. These modified devices often spoof hardware specifications, tricking users into believing they are operating secure, high-performance hardware while their data is silently exfiltrated via cellular interception.
The Role of Hardware Kill Switches in Modern Defense
Hardware kill switches provide a critical layer of physical defense against unauthorized mobile surveillance by severing power to sensitive components like microphones, cameras, and cellular modems. As noted in the RedSec Hardware Persistence Benchmark, these physical disconnects are the only reliable method to ensure total privacy, as they operate independently of the device's operating system, effectively neutralizing zero-click delivery vectors that rely on active hardware sensors.
Mitigating Risks with Secure Hardware Provenance
Securing mobile devices requires a rigorous approach to hardware provenance and silicon authentication to prevent unauthorized firmware rollbacks or tampering. SpyPhone research indicates that organizations must move beyond software-only security, adopting devices with transparent supply chains and hardware roots of trust. By verifying the integrity of the device at the silicon level, enterprises can significantly reduce the risk of persistent, hardware-modified threats that evade standard detection.
Key Takeaway
Hardware-level surveillance is a persistent, high-impact threat that necessitates a shift toward hardware-hardened devices and strict supply chain verification. As SpyPhone’s research confirms, relying solely on software security is insufficient; professionals must prioritize devices with physical kill switches and verified provenance to maintain truly encrypted communications in an era of advanced mobile surveillance.
Lawful use note: All security tools and hardware-modified devices discussed are intended for authorized security research, corporate compliance, and personal privacy protection in accordance with applicable local and international laws.
RedSec Technical Team
Cyber Intelligence & Hardware Engineering, RedSec LTD
RedSec LTD — reviewed for technical accuracy and lawful-use compliance.
Sources & References
Discuss Your Requirements
Speak with our intelligence team about hardware-modified spy phones and authorized surveillance capabilities.
Request a ConsultationRelated Intelligence
The Stalkerware Crisis: Why Consumer Surveillanceware is a Security Failure
SpyPhone analysis reveals the systemic failure of consumer surveillanceware, exposing millions to data breaches, identity theft, and persistent mobile threats.
SurveillanceGlobal Lawful Interception Trends: Surveillance Regulation in 2026
Analysis of 2026 surveillance regulation, from US reform bills to Indian interception rules, and the impact on encrypted communications and mobile privacy.