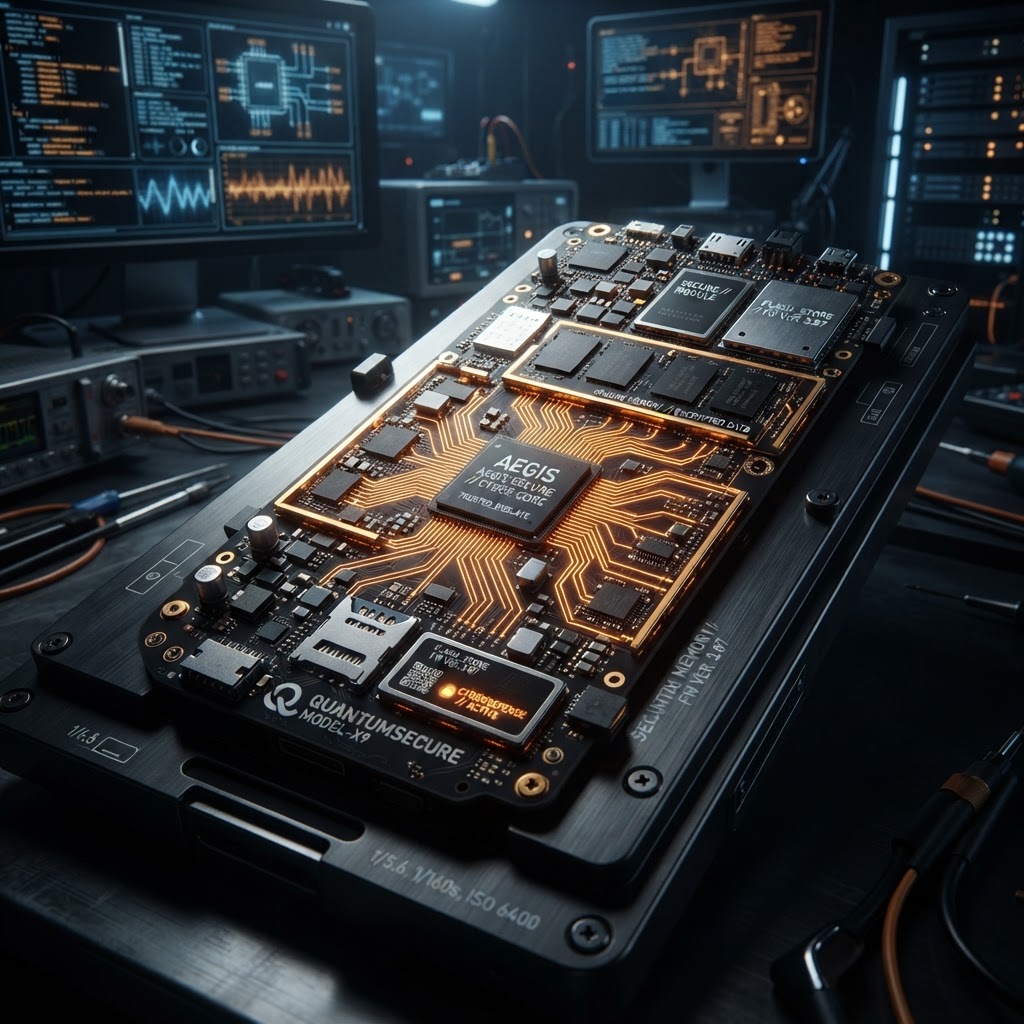
The Evolution of Hardware-Level Surveillance and Mobile Threats. In the current threat landscape, the distinction between software-based mobile malware and hardware-level surveillance is rapidly dissolving. As mobile forensics capabilities advance, threat actors are increasingly moving beyond traditional application-layer exploits to target the very silicon and firmware that power our devices. This shift represents a critical escalation in mobile surveillance, where the device itself becomes a compromised asset, often bypassing standard security protocols. For professionals relying on encrypted communications, understanding these hardware-centric vectors is no longer optional; it is a fundamental requirement for operational security. ## Analyzing the Manic Android Threat and Offline Exfiltration. Recent intelligence regarding the 'Manic' Android malware highlights a dangerous trend: the ability to exfiltrate data from offline devices by leveraging nearby infected hardware. This capability demonstrates how modern spyware for phones can bridge the gap between isolated networks and external command-and-control infrastructure. By utilizing proximity-based communication protocols, Manic effectively turns a compromised handset into a node for data relay, complicating traditional network-based detection. This evolution underscores why standard mobile security suites often fail to detect sophisticated, hardware-aware threats that operate beneath the operating system's visibility. ## Cellular Interception and Network-Level Vulnerabilities. While device-level security is paramount, we must also address the persistent threat of cellular interception. Surveillance vendors continue to exploit legacy signaling protocols like SS7 to track mobile devices through carrier networks. Unlike zero-click exploits that target specific software vulnerabilities, these network-level attacks are often invisible to the end-user. When a device is targeted via its carrier, the SIM card itself can be instructed to report location data, effectively turning the phone into a tracking beacon. For those requiring high-assurance security, relying solely on software-based encryption is insufficient; one must consider the integrity of the entire communication chain, including the hardware and the network path. ## Mitigating Risks with Hardened Infrastructure. The proliferation of hardware-modified phones serves as a necessary countermeasure for high-risk individuals. By stripping away unnecessary sensors, disabling microphones, and implementing hardware-level kill switches, these devices minimize the attack surface available to sophisticated spyware. When integrated with a secure C2 dashboard for real-time monitoring and threat response, these solutions provide a robust defense against the persistent surveillance campaigns often associated with a Pegasus spyware alternative. As manufacturers like Apple attempt to mitigate covert recording through software chimes and visual indicators, the professional sector must continue to prioritize hardware-level integrity to ensure true privacy. ## Key Takeaway. The convergence of hardware-level surveillance and advanced mobile malware necessitates a shift toward hardware-hardened devices and network-agnostic communication strategies to maintain operational security in an increasingly hostile digital environment. All security tools and hardware modifications discussed herein are intended for lawful use in authorized security, investigative, and compliance contexts only.
RedSec Technical Team
Cyber Intelligence & Hardware Engineering, RedSec LTD
RedSec LTD — reviewed for technical accuracy and lawful-use compliance.
Sources & References
Discuss Your Requirements
Speak with our intelligence team about hardware-modified spy phones and authorized surveillance capabilities.
Request a ConsultationRelated Intelligence
Spyware Analysis
The State of Commercial Spyware: Pegasus and the Global Surveillance Crisis
An in-depth analysis of the commercial spyware market, Pegasus litigation, and the evolving threat of zero-click mobile surveillance in 2026.
Threat IntelligenceMDM Vulnerabilities and the Escalating Threat to Enterprise Mobile Security
Explore how recent MDM zero-days and macOS privilege escalation flaws are reshaping enterprise mobile security, encryption standards, and threat mitigation.