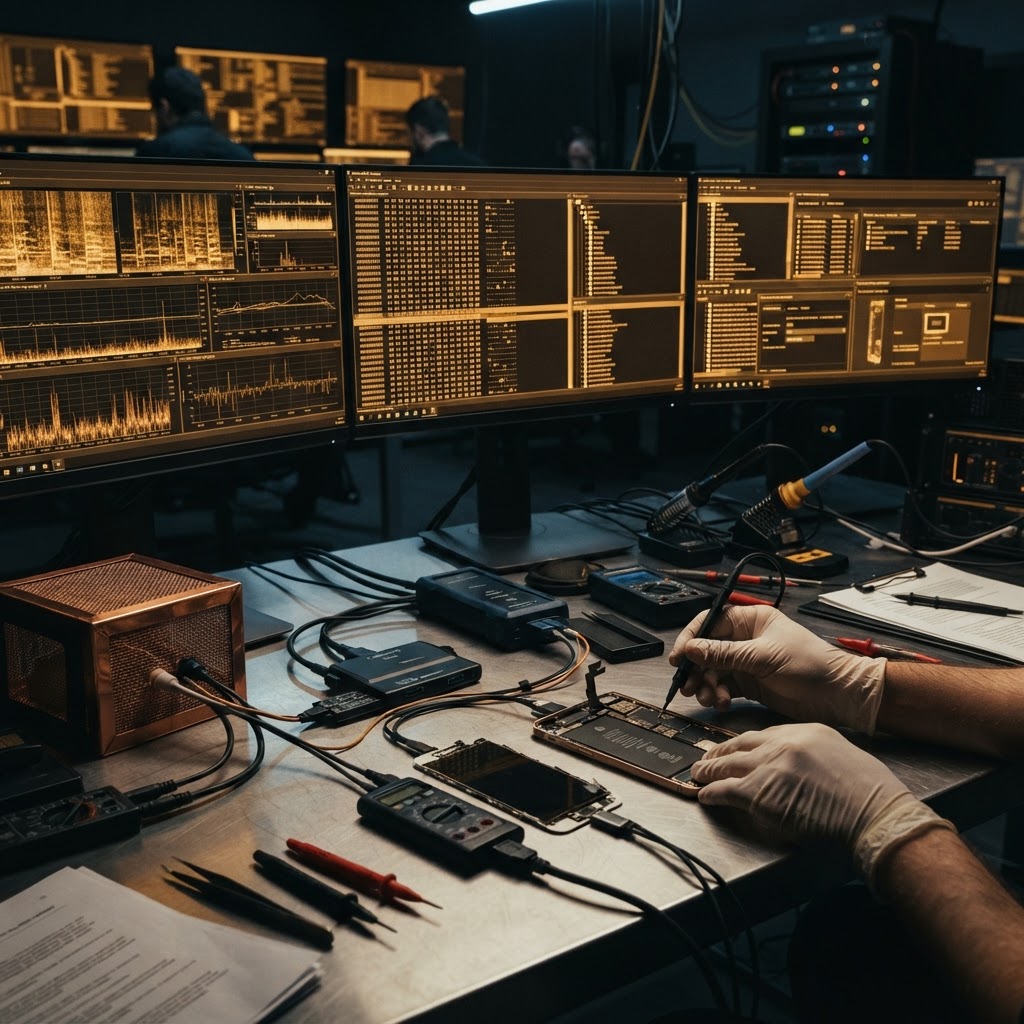
The Expanding Battlefield of Mobile Forensic Analysis
Mobile forensics is the systematic recovery, acquisition, and technical examination of digital evidence stored on smartphones, tablets, and cellular connected devices. As enterprise investigations and high-stakes audits face increasingly hostile threat landscapes, mobile forensics has transitioned from simple physical extraction to deep, non-volatile and volatile memory triage. Sophisticated adversaries deploy nation-state mercenary tooling and customized implants capable of bypassing standard on-device anti-malware protections.
Recent investigative releases from threat research teams—including Citizen Lab, the SHARE Foundation, and Amnesty International’s Security Lab—illustrate this escalation. Targeted operations leveraging iMessage zero-click exploits and stealthy, localized Android variants such as newly surfaced iterations of NoviSpy demonstrate how threat actors routinely tailor cellphone spyware to circumvent known Indicators of Compromise (IOCs). In zero-click attacks, an adversary achieves remote code execution without user interaction, requiring investigators to scrutinize microscopic logging artifacts across cellular subsystems, background services, and kernel queues.
For corporate risk officers, compliance investigators, and security researchers, baseline threat intelligence is no longer sufficient. Detecting modern mobile surveillance requires specialized forensic frameworks that analyze encrypted storage snapshots, parse unallocated flash sectors, and reconstruct real-time execution chains.
Unmasking Zero-Click Exploitation: MVT and Advanced Artifact Extraction
Commercial spyware campaigns notoriously abuse vulnerabilities in native message-processing and media-parsing engines. When an exploit payload lands via SMS, MMS, or instant messaging, standard consumer operating systems obscure the breach behind aggressive application sandboxing. Consequently, static file scanning rarely identifies commercial mercenary malware.
Advanced toolsets like the Mobile Verification Toolkit (MVT), originally established during the Pegasus Project investigations, have set the modern precedent for forensic triage. Rather than treating mobile devices as static disk storage, forensic utilities must extract system backups, diagnostic logs (sysdiagnose files on iOS), and Android Package Manager dumps. Investigators isolate anomalous behaviors by cross-referencing timeline structures against known adversary infrastructures, matching HTTP requests, process crash logs, and localized database anomalies:
- Safari and WebKit Records: Examining local cache records and IndexedDB states for unauthorized domain redirection or memory-allocation anomalies.
- Service Management Traces: Auditing persistent daemons and scheduled tasks via
launchdartifacts on iOS orinitservices on Android. - Cellular and Messaging DBs: Inspecting Core Data artifacts (
sms.db, Call History stores) for silent injection vectors where zero-interaction payloads drop silently onto the device.
Because top-tier threat vendors implement defensive counter-forensics that purge intermediate payload files from non-volatile memory, analysts increasingly rely on heuristic detection rather than exact hash matches. The emergence of a viable Pegasus spyware alternative in the commercial gray market highlights the need for continuous pipeline updates across forensic suites like MSAB XRY, Magnet AXIOM, MOBILedit Forensic, and Cellebrite.
Fileless Mobile Malware and Volatile Memory Challenges
One of the most complex hurdles facing modern forensic specialists is the rise of fileless and purely memory-resident mobile malware. By executing malicious payloads directly within volatile memory (RAM) and hooking existing legitimate process memory, attackers significantly reduce persistent disk footprints. If an investigator powers off an infected phone or triggers a cold reboot, the volatile state vanishes, degrading critical operational evidence.
Forensic toolchains counter this evasive behavior through several modern techniques:
- Live Network Forensics and Bridge Interception: Capturing encrypted device traffic via hardware-bridged network listeners. Even when implants tunnel telemetry to an adversary's C2 dashboard through TLS/SSL pinners, metadata patterns, heartbeat intervals, and unusual handshake protocols reveal persistent remote access.
- Runtime Memory Acquisition: Leveraging specialized software agents to extract memory segments from compromised background processes before initiating device shutdown.
- Hardware-Level Extraction: Utilizing low-level system loader interfaces (e.g., EDL on Qualcomm chips, BootROM hooks) to capture direct physical flash dumps before the operating system's internal encryption partitions lock permanently.
Understanding these operational vectors is essential when assessing high-value endpoints. In scenarios where software-based isolation can be systematically undermined, security-first organizations mitigate risk by turning to hardware-modified phones, physically disconnecting microphones, camera modules, and cellular telemetry lines to neutralize hardware surveillance vectors that software triage might fail to observe.
Defending Against Cellular Interception and Inter-System Telemetry
Forensic scrutiny does not stop at internal storage. Cellular interception via rogue base stations—commonly termed IMSI catchers or Stingrays—remains a major blind spot for standard forensic toolchains. Rogue cell towers exploit lower-layer telecommunications vulnerabilities (in 2G, 3G, and poorly configured LTE/5G handover protocols) to downgrade encryption, intercept SMS-based secondary authentication, and triangulate physical location.
To bridge this forensic visibility gap, mobile forensics pipelines are integrating real-time baseband monitoring tools. Software-defined radios (SDRs) paired with telecom-aware anomaly engines trace unauthorized downgrade commands, inconsistent Cell IDs, and anomalous signal strength spikes indicative of localized cellular interception. Countering this exposure requires the strict enforcement of zero-trust policies, the adoption of robust encrypted communications protocols resistant to baseband eavesdropping, and end-to-end device audits conducted inside strict RF-shielded environments (Faraday isolation).
Key Takeaway
As zero-click payloads, memory-only execution, and bespoke commercial surveillance packages evolve, single-pane signature scanners are obsolete. True mobile forensics demands an integrated methodology: combining timeline-based artifact triage, network-level telemetry monitoring, and low-level physical acquisition to unmask advanced threats before sensitive corporate and legal assets are permanently compromised.
Notice: Digital forensics, device monitoring, and technical signal analysis must be conducted in strict compliance with applicable statutory authorizations, organizational compliance standards, and lawful data privacy regulations.
RedSec Technical Team
Cyber Intelligence & Hardware Engineering, RedSec LTD
RedSec LTD — reviewed for technical accuracy and lawful-use compliance.
Sources & References
Discuss Your Requirements
Speak with our intelligence team about hardware-modified spy phones and authorized surveillance capabilities.
Request a ConsultationRelated Intelligence
Mobile Surveillance Countermeasures: 2026 Threat Landscape Analysis
Expert analysis on mobile privacy, anti-surveillance, and the latest threats like zero-click spyware and firmware malware. Protect your encrypted communications.
Cellular InterceptionSS7 and IMSI Catcher Threats: The 2026 Mobile Surveillance Landscape
Analysis of 2026 cellular interception trends, covering SS7/Diameter vulnerabilities, passive IMSI catching, and the rise of covert telecom surveillance campaigns.