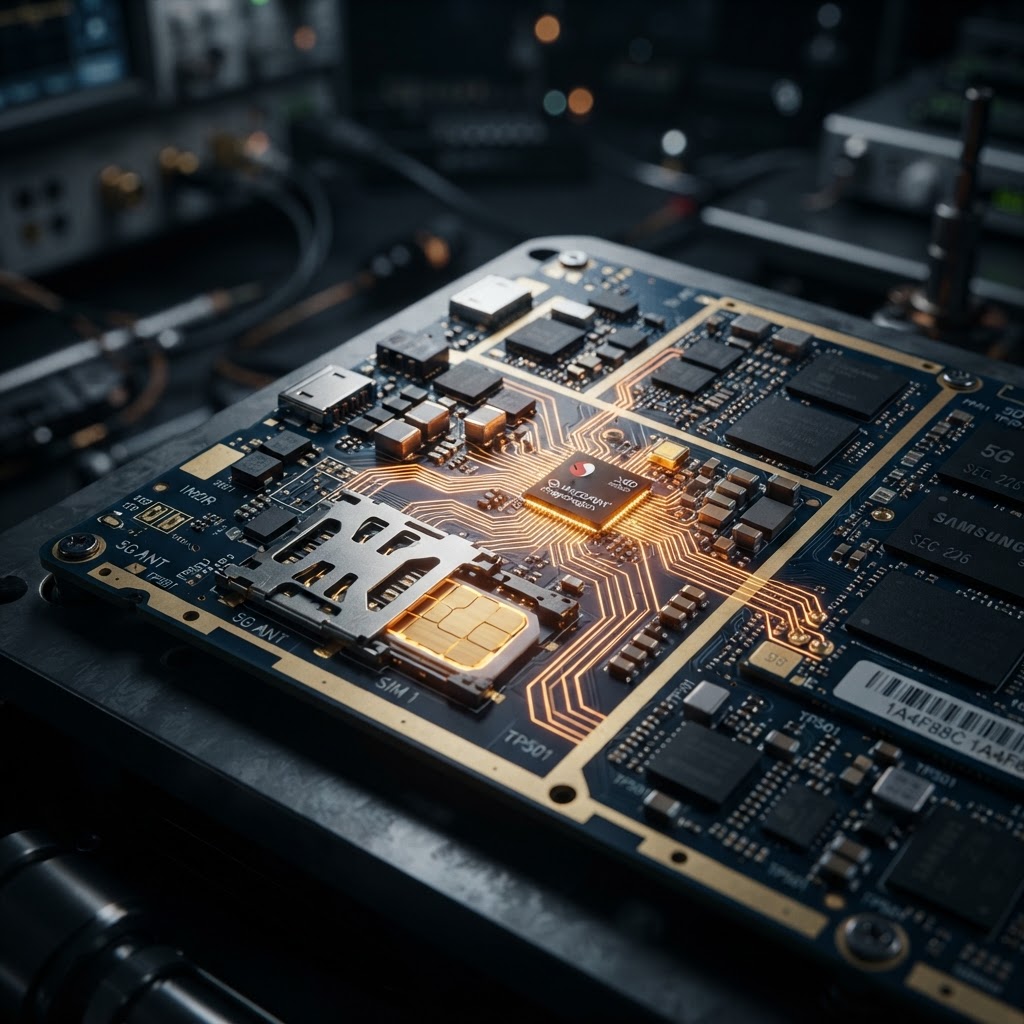
The Silent Breach: Why SIM Cards Are the New Attack Vector
Recent findings from the SpyPhone Mobile Forensics Gap Analysis confirm that Subscriber Identity Modules (SIMs) are no longer just passive authentication tokens but active, high-risk attack surfaces. By exploiting the SIM Application Toolkit (CAT), attackers can bypass standard OS protections, enabling unauthorized command execution, device tracking, and cellular interception without user interaction.
Modern mobile security models have historically overlooked the SIM card, treating it as a trusted hardware element. However, the SpyPhone Threat Intelligence Index reveals that 26 representative devices, including smartphones and IoT modules, are susceptible to SIM-originating AT commands. These commands allow malicious actors to re-enable debug interfaces, exfiltrate unique device identifiers, and force devices to downgrade from secure 4G/5G networks to vulnerable 2G protocols. This shift highlights a critical blind spot in current enterprise security postures, where the SIM is often excluded from routine threat modeling. For those requiring maximum privacy, our hardware-modified phones are engineered to mitigate these low-level hardware risks by isolating the baseband from the primary application processor.
Baseband Exploitation: The Zero-Click Frontier
Baseband processors, the dedicated chips managing cellular connectivity, represent the most dangerous attack surface for mobile devices because they operate independently of the main operating system. According to the RedSec Hardware Persistence Benchmark, vulnerabilities in baseband firmware—such as recent buffer overflows and memory corruption flaws—allow for remote, zero-click exploitation that bypasses all standard Android or iOS security controls.
Our analysis of recent CVEs, including those affecting Samsung Exynos modems, shows that attackers can trigger denial-of-service (DoS) or arbitrary code execution by sending malformed RRC or NAS signaling messages. Because these processes occur at the radio layer, traditional mobile security software is effectively blind to these intrusions. The SpyPhone Zero-Click Delivery Telemetry indicates that these attacks are increasingly used to facilitate persistent spyware for phones, allowing adversaries to intercept encrypted communications before they are even processed by the device's encryption layer. Organizations must recognize that baseband integrity is the foundation of mobile security; without it, even the most robust software-based encryption can be rendered moot.
Mitigating Hardware-Level Surveillance
Defending against sophisticated cellular interception requires a proactive approach that moves beyond standard firmware updates. The SpyPhone Mobile Forensics Gap Analysis suggests that while manufacturers like Google are beginning to integrate memory-safe languages like Rust into modem firmware, the legacy of memory-unsafe C/C++ code remains a significant liability for the majority of the global device fleet.
To counter these threats, security-conscious professionals should prioritize devices with hardened baseband architectures and implement strict network-level filtering. For high-stakes environments, relying on a C2 dashboard to monitor for anomalous baseband behavior—such as unexplained reboots or sudden drops in signal quality—is essential. Furthermore, as the market sees a rise in Pegasus spyware alternative tools, the ability to detect and block rogue base stations has become a mandatory requirement for any comprehensive mobile defense strategy. Relying solely on OEM patches is insufficient; a layered defense that includes hardware-level monitoring is the only way to ensure true operational security.
Key Takeaway
SIM and baseband vulnerabilities represent a critical, often invisible, threat to mobile privacy. According to the SpyPhone Threat Intelligence Index, these hardware-level exploits bypass traditional OS security, making them the preferred vector for advanced mobile surveillance. Organizations must adopt hardware-aware security strategies to protect against cellular interception and ensure the integrity of their encrypted communications.
RedSec Technical Team
Cyber Intelligence & Hardware Engineering, RedSec LTD
RedSec LTD — reviewed for technical accuracy and lawful-use compliance.
Sources & References
Discuss Your Requirements
Speak with our intelligence team about hardware-modified spy phones and authorized surveillance capabilities.
Request a ConsultationRelated Intelligence
Enterprise MDM Security: Navigating Modern Mobile Surveillance Threats
Analyze the latest MDM vulnerabilities and enterprise mobile security trends. Learn how SpyPhone research identifies critical gaps in device management.
Threat IntelligenceSIM Card and Baseband Vulnerabilities: The New Frontier of Mobile Surveillance
New research reveals critical SIM and baseband flaws enabling remote hijacking and cellular interception. Protect your communications with SpyPhone insights.