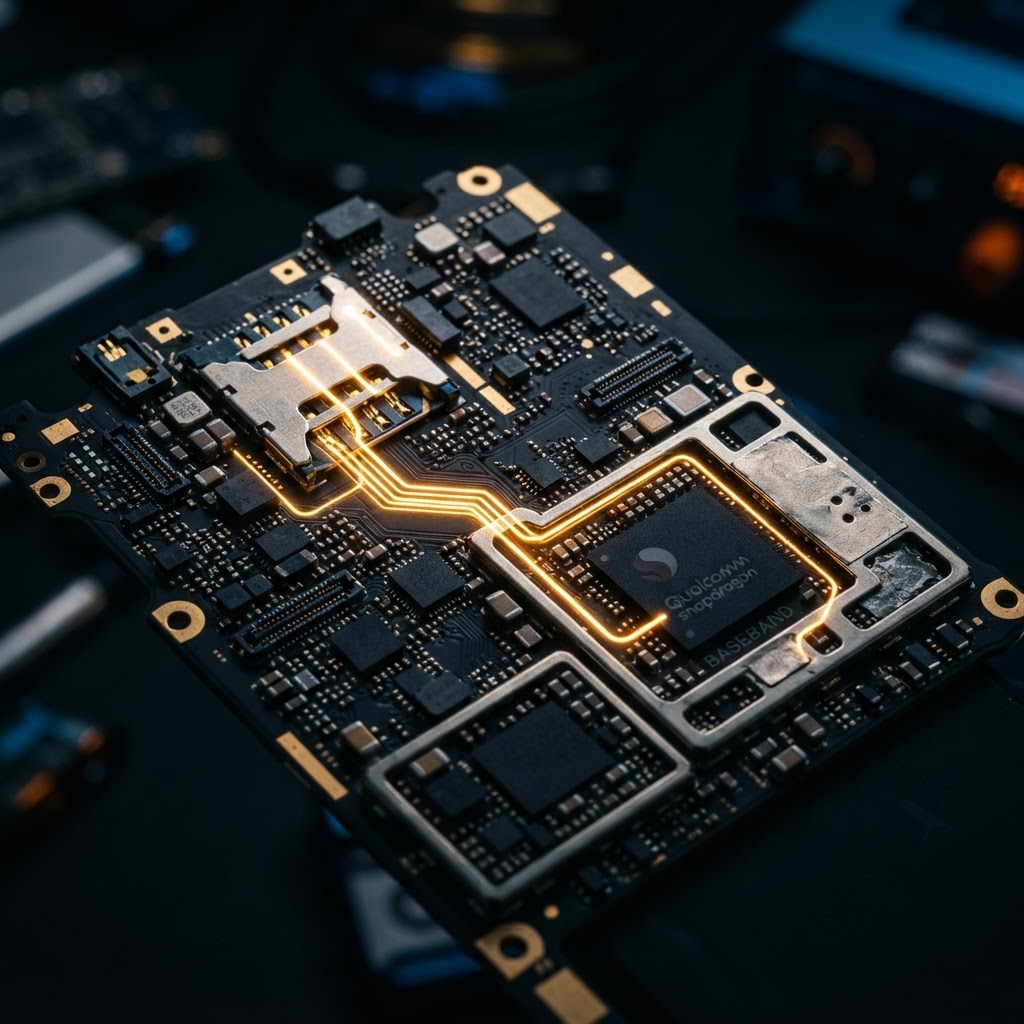
The Silent Threat: Baseband and SIM Vulnerabilities
The cellular baseband—the dedicated processor responsible for managing radio communications, network handovers, and signal timing—has become a primary target for sophisticated threat actors. Because the baseband operates independently of the main operating system, it often lacks the robust security guardrails found in modern application processors. Recent research highlights that vulnerabilities in these modems, manufactured by industry leaders like Samsung, MediaTek, and Qualcomm, allow for remote code execution and stealthy cellular interception. By exploiting these flaws, attackers can downgrade a device's connection from 5G to legacy protocols, facilitating eavesdropping and the injection of malicious traffic without user interaction.
SIM Card Exploitation and Zero-Click Risks
SIM cards are frequently perceived as trusted hardware, yet they remain a critical vector for mobile surveillance. Vulnerabilities in the SIM Toolkit (STK) and the S@T Browser application allow attackers to send specially crafted, invisible SMS messages to a target device. This zero-click attack vector can trigger the SIM to execute commands, such as requesting location data or exfiltrating sensitive information, all without the user's knowledge. Unlike traditional spyware for phones, these SIM-level exploits leave virtually no trace in the device's standard application logs, making them a preferred tool for high-stakes espionage.
The Intersection of Hardware and Mobile Forensics
For corporate and investigative professionals, understanding the distinction between software-based mobile malware and hardware-level compromise is essential. While hardware-modified phones can provide a layer of physical security, the underlying baseband remains a complex attack surface. Forensic experts must now account for baseband artifacts when conducting investigations, as these logs can reveal anomalies in network registration that indicate a compromise. Relying on standard extraction tools is often insufficient; advanced mobile forensics requires a deep dive into the radio-control functions to identify if a device has been subjected to a baseband-level attack.
Mitigating Risks in Encrypted Communications
To maintain the integrity of encrypted communications, organizations must move beyond simple software-based encryption. The persistence of vulnerabilities in cellular infrastructure—such as the aging SS7 protocol—means that even secure messaging apps can be undermined if the underlying cellular connection is compromised. Implementing a C2 dashboard for fleet management and utilizing devices with hardened modems are critical steps in defending against these persistent threats. For those seeking a Pegasus spyware alternative in terms of defensive posture, prioritizing devices that allow for granular control over baseband connectivity is the new standard for high-security operations.
Key Takeaway
SIM and baseband vulnerabilities represent a critical, often overlooked layer of mobile risk; securing modern communications requires a defense-in-depth strategy that accounts for both hardware-level exploits and the inherent weaknesses of global cellular networks.
Note: All security tools and techniques discussed are intended for lawful use in authorized security research, corporate compliance, and private investigative contexts only.
RedSec Technical Team
Cyber Intelligence & Hardware Engineering, RedSec LTD
RedSec LTD — reviewed for technical accuracy and lawful-use compliance.
Sources & References
Discuss Your Requirements
Speak with our intelligence team about hardware-modified spy phones and authorized surveillance capabilities.
Request a ConsultationRelated Intelligence
SS7 and IMSI Catcher Threats: The 2026 Mobile Surveillance Landscape
SpyPhone analysis of the latest SS7 and IMSI catcher developments. Learn how modern mobile surveillance exploits signaling protocols to track and intercept.
Threat IntelligenceMobile Threat Intelligence: APT Campaigns and Surveillance Trends 2026
Explore the latest mobile threat intelligence on APT campaigns, zero-click exploits, and mobile malware targeting high-profile individuals and enterprise users.