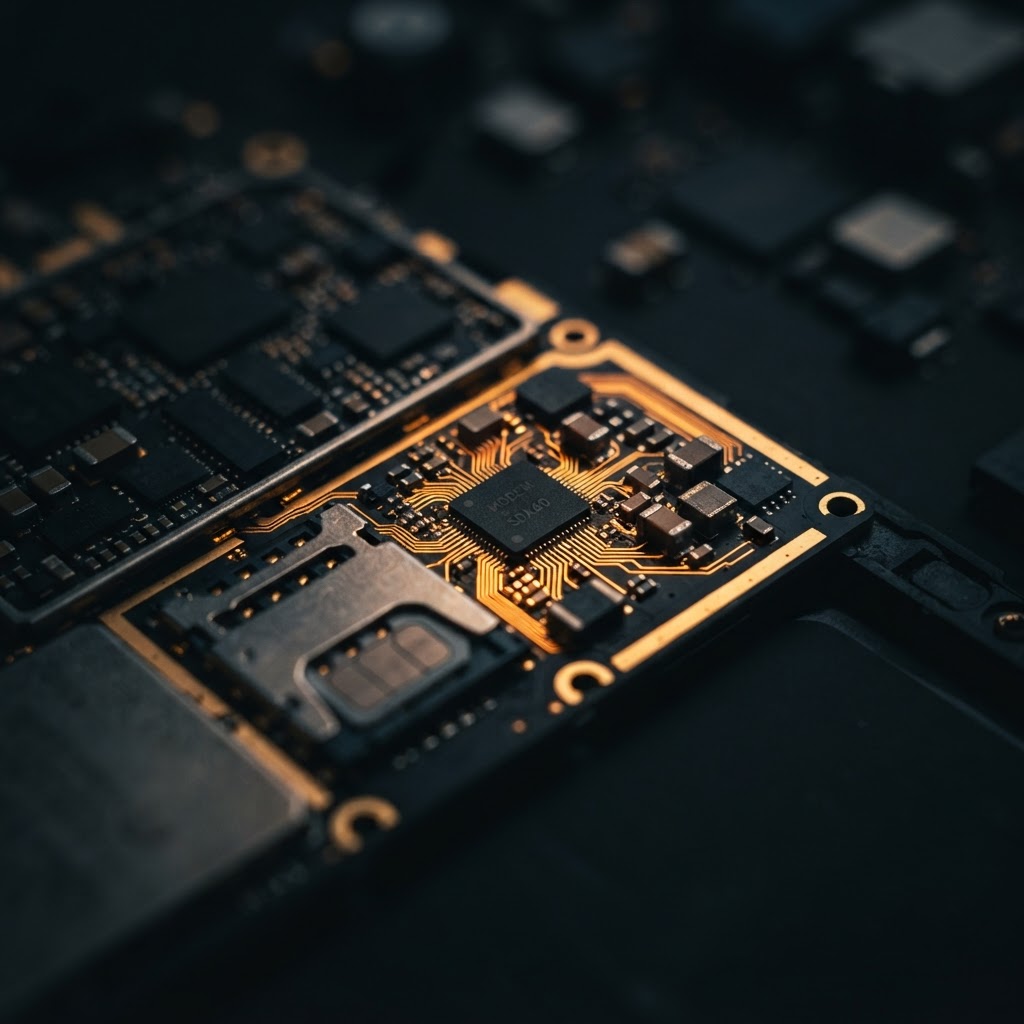
The Invisible Attack Surface: SIM and Baseband Risks
Modern mobile security is often focused on the application layer, yet the most critical vulnerabilities frequently reside in the hardware and firmware layers that users cannot easily audit. Recent research presented at the USENIX WOOT Conference highlights that Subscriber Identity Module (SIM) cards are not merely passive storage chips but fully functional mini-computers capable of running applications. When these cards are compromised, they become potent tools for mobile surveillance. Simultaneously, the cellular baseband—the dedicated processor responsible for managing LTE, 4G, and 5G communications—remains a high-risk attack surface. Because the baseband must process untrusted inputs from cellular towers, it is uniquely susceptible to remote code execution (RCE) attacks that require no user interaction, often referred to as zero-click exploits.
Baseband Hardening and the Evolution of Modem Security
Recent industry shifts, such as the security hardening implemented in the Google Pixel 9, underscore the severity of baseband-level threats. Historically, basebands have lacked the robust exploit mitigations found in application processors, making them a primary target for cellular interception. Attackers can leverage false base stations to inject malicious network packets, potentially gaining control over the device's modem firmware. This allows for the silent monitoring of communications. For professionals relying on encrypted communications, a compromised baseband can bypass software-level encryption by intercepting data before it is encrypted or after it is decrypted by the application processor. This reality has driven the demand for hardware-modified phones that prioritize baseband isolation and firmware integrity.
The SIM Card as a Vector for Remote Exploitation
Beyond the baseband, the SIM card itself has emerged as a sophisticated vector for compromise. Vulnerabilities such as those identified in recent academic research (e.g., CVE-2024-27209) demonstrate that attackers can send specially crafted SMS messages to trigger unauthorized actions on the SIM card. These actions can range from tracking a user's physical location to intercepting sensitive data. The transition to eSIM technology, while offering convenience, introduces new attack vectors where criminals can remotely port numbers or manipulate digital profiles. Organizations must recognize that traditional two-factor authentication tied to a phone number is increasingly fragile against these advanced SIM-based attacks. For high-stakes environments, moving away from standard consumer-grade SIM management toward private network solutions or specialized C2 dashboard monitoring is becoming a standard compliance requirement.
Mitigating Risks in a Hostile Cellular Environment
As mobile malware becomes more adept at exploiting the gap between the baseband and the operating system, the industry is seeing a surge in privacy-first infrastructure. Companies are now investing heavily in mobile virtual network operators (MVNOs) that embed security directly into the network layer, effectively creating a buffer against common cellular interception techniques. When selecting mobile hardware, professionals should prioritize devices that receive frequent, verified baseband updates and offer granular control over cellular connectivity. Relying on standard consumer devices for sensitive operations is increasingly viewed as a liability, leading many to seek a Pegasus spyware alternative in the form of hardened, privacy-centric mobile ecosystems that mitigate the risk of zero-click baseband exploitation.
Key Takeaway
SIM and baseband vulnerabilities represent a critical, often overlooked, tier of mobile risk that can facilitate silent, zero-click surveillance; securing these layers requires a shift toward hardware-hardened devices and network-level security controls.
All security tools and hardware-modified devices discussed herein are intended for use in accordance with applicable local, state, and federal laws regarding privacy and electronic communications.
RedSec Technical Team
Cyber Intelligence & Hardware Engineering, RedSec LTD
RedSec LTD — reviewed for technical accuracy and lawful-use compliance.
Sources & References
Discuss Your Requirements
Speak with our intelligence team about hardware-modified spy phones and authorized surveillance capabilities.
Request a ConsultationRelated Intelligence
Mobile APT Campaigns Surge: The New Reality of Persistent Surveillance
Advanced Persistent Threats are shifting to mobile-first strategies. Discover how modern mobile malware and zero-click exploits are reshaping global security.
SurveillanceHardware-Level Surveillance: The New Frontier of Mobile Compromise
Explore the rise of hardware-level surveillance and modified devices. Learn how modern threats bypass traditional security to compromise mobile integrity.