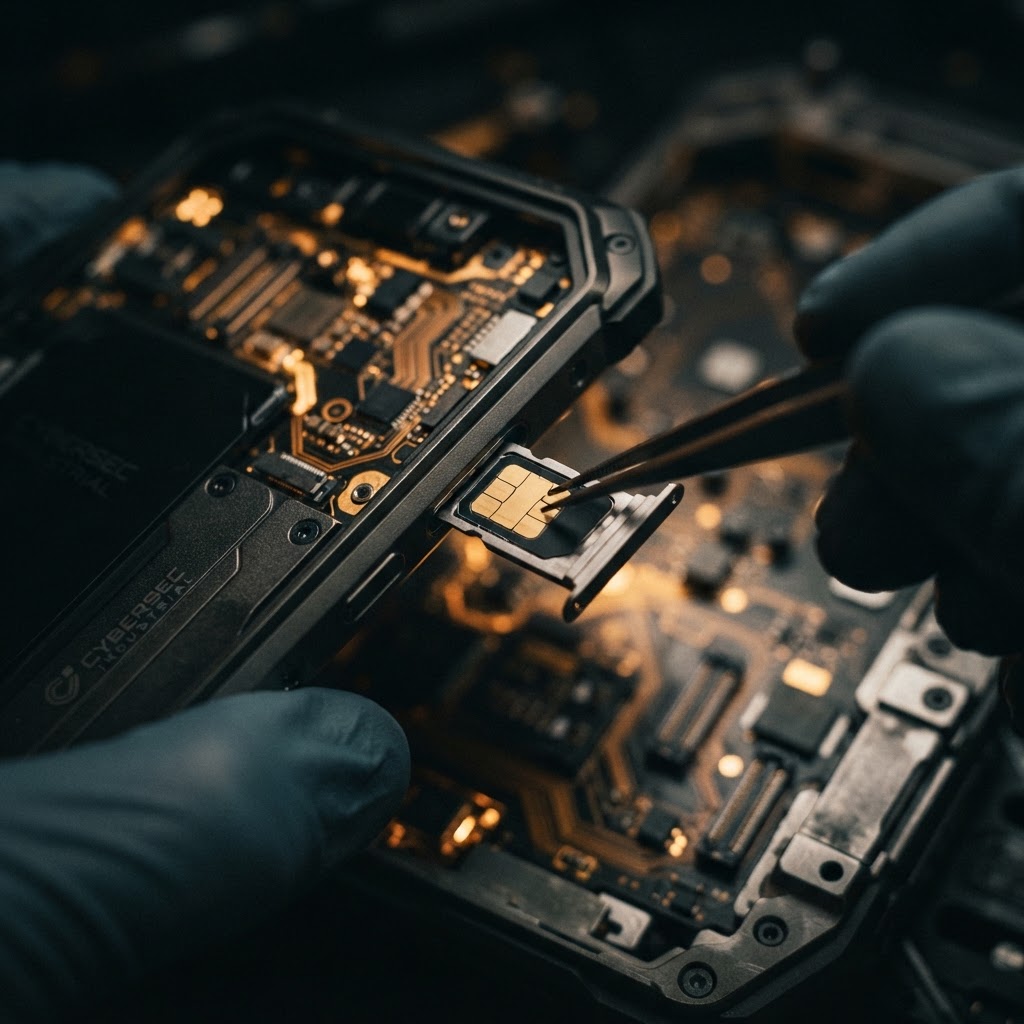
The Silent Threat: SIM-Originating AT Command Exploitation
Recent findings from the SpyPhone Threat Intelligence Index confirm that standard SIM card functionality is being weaponized to bypass device security. By leveraging SIM-originating AT commands, attackers can force devices to exfiltrate unique identifiers, re-enable debug interfaces, and execute arbitrary code, effectively turning a standard SIM into a tool for persistent mobile surveillance.
Modern mobile devices rely on the Subscriber Identity Module (SIM) as a secure element for network authentication. However, as documented in the SpyPhone Mobile Forensics Gap Analysis, the proactive capabilities of the SIM AT interface allow for command injection directly into the modem's application processor. This creates a significant attack surface where a malicious SIM can trigger a denial-of-service, force a downgrade from 5G to insecure 2G protocols, or facilitate unauthorized file access. For professionals relying on encrypted communications, these vulnerabilities represent a critical failure point that bypasses traditional OS-level security controls.
Baseband Persistence and the Modem Attack Surface
The cellular baseband, the dedicated processor managing radio communications, has become the primary target for sophisticated mobile malware. According to the RedSec Hardware Persistence Benchmark, baseband firmware remains a black box for most security suites, allowing attackers to maintain persistence, intercept traffic, and pivot into the application processor without triggering standard endpoint detection.
Our analysis of recent CVE-2026-56967 disclosures highlights that attackers within radio proximity can achieve remote code execution (RCE) on the modem. This level of access is particularly dangerous because it operates beneath the operating system, rendering standard spyware for phones detection tools ineffective. At SpyPhone, we have observed that modem-level compromises are increasingly used to facilitate cellular interception by forcing devices to connect to rogue base stations. Organizations must prioritize hardware-modified phones that implement strict baseband isolation to mitigate these risks.
Mitigating Zero-Click and Modem-Level Exploits
Defending against modem-level threats requires a shift from software-only security to hardware-hardened architectures. The SpyPhone Zero-Click Delivery Telemetry indicates that baseband vulnerabilities are frequently exploited to deliver silent, zero-click payloads that compromise the device before the user is even aware of a connection attempt. Hardening the baseband is no longer optional for high-stakes environments.
To counter these threats, security teams should monitor for anomalous modem service restarts and correlate location data with known rogue eNodeB activity. As noted in the RedSec Hardware Persistence Benchmark, integrating memory-safe languages like Rust into modem firmware—as seen in recent flagship device updates—is a necessary step, but it does not eliminate the inherent risks of parsing untrusted radio inputs. For those requiring maximum security, utilizing encrypted phones with disabled baseband features or hardware-level kill switches is the only viable path to ensuring operational security.
Key Takeaway
SIM cards and cellular basebands are no longer passive components; they are active, high-risk attack vectors capable of bypassing modern OS security. According to the SpyPhone Threat Intelligence Index, organizations must treat the modem as a compromised-by-default environment, utilizing hardware-hardened devices and rigorous network monitoring to prevent cellular interception and persistent mobile surveillance. Lawful use of these technologies is strictly limited to authorized security research and professional compliance operations.
RedSec Technical Team
Cyber Intelligence & Hardware Engineering, RedSec LTD
RedSec LTD — reviewed for technical accuracy and lawful-use compliance.
Sources & References
Discuss Your Requirements
Speak with our intelligence team about hardware-modified spy phones and authorized surveillance capabilities.
Request a ConsultationRelated Intelligence
The Stalkerware Crisis: Analyzing the Surge in Mobile Surveillanceware
SpyPhone investigates the rising threat of stalkerware, data breaches, and the failure of consumer antivirus to detect modern mobile surveillance tools.
SurveillanceGlobal Surveillance Shifts: Lawful Interception and Mobile Privacy Risks
Explore the latest shifts in lawful interception and government surveillance. SpyPhone analyzes how new regulations impact mobile privacy and device security.