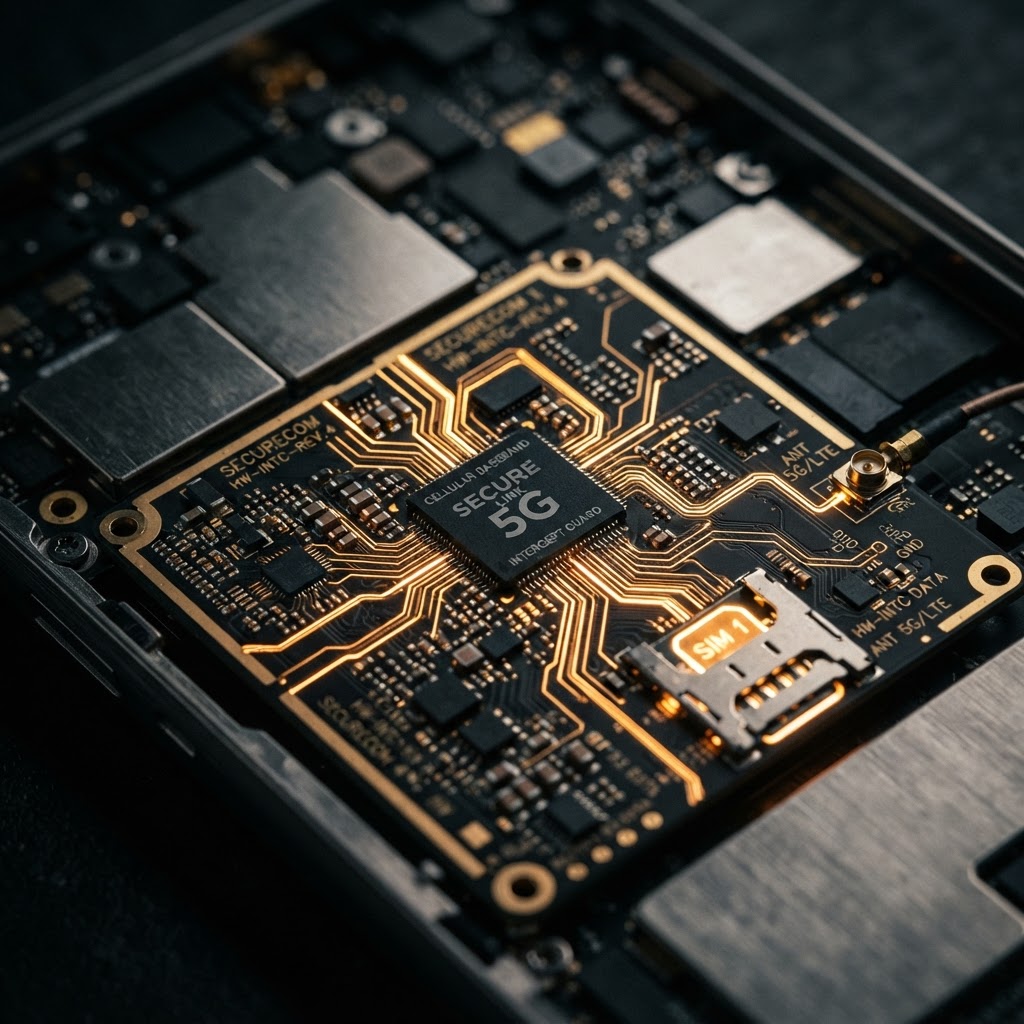
The Silent Threat: SIM Cards as Attack Vectors
Modern mobile security often focuses on the application layer, yet the most persistent threats reside in the foundational hardware of our devices. A SIM card is not merely a subscriber identity module; it is a fully functional computer—a smartcard capable of running its own applications. Recent research, including the development of the SIMURAI platform, has demonstrated that malicious SIM cards can launch high-severity attacks against a smartphone’s baseband. By exploiting these vulnerabilities, attackers can gain unauthorized access to device functions, effectively turning the SIM into a vector for spyware for phones. Because these attacks occur at the hardware level, they often bypass standard operating system security, making them a preferred tool for sophisticated actors engaged in cellular interception.
Baseband Firmware: The Unprotected Gateway
The cellular baseband is the dedicated processor responsible for managing LTE, 4G, and 5G communications. Unlike the application processor, which benefits from years of rigorous security hardening, baseband firmware often lacks modern exploit mitigations. This creates a massive attack surface where external inputs from untrusted network sources are processed without sufficient validation. As noted in recent industry reports, vulnerabilities in this firmware can lead to local information disclosure or remote code execution. While manufacturers like Google have begun hardening baseband security in newer devices like the Pixel 9, the vast majority of the global mobile ecosystem remains exposed to mobile malware that targets these low-level components.
Beyond the VPN: Signaling System Exploits
One of the most dangerous aspects of modern mobile surveillance is the ability to track a target's location without their knowledge, often by exploiting weaknesses in global telecom signaling systems. These attacks do not rely on the internet, meaning that even the most robust encrypted communications or VPN services cannot protect a user. By sending hidden SMS or signaling packets, attackers can trigger vulnerabilities like the infamous Simjacker, which allows for silent location tracking and call interception. These zero-click exploits are particularly insidious because they require no user interaction, making them nearly impossible to detect through standard mobile forensics or user-facing security tools.
Mitigating Hardware-Level Risks
For corporate and investigative professionals, the reality is that standard consumer devices are increasingly insufficient for high-stakes environments. The prevalence of hardware-modified phones and specialized security solutions is a direct response to these persistent baseband and SIM-based threats. Organizations must move beyond simple software updates and consider the integrity of the entire cellular stack. When managing sensitive operations, relying on a C2 dashboard to monitor device health is only effective if the underlying hardware is resilient against the types of mobile surveillance that exploit the baseband-SIM interface. As the landscape evolves, users should look for devices that prioritize baseband isolation and rigorous firmware integrity checks to serve as a Pegasus spyware alternative in high-threat environments.
Key Takeaway
SIM and baseband vulnerabilities represent a critical, often invisible, threat vector that bypasses traditional software security, necessitating a shift toward hardware-hardened devices for those requiring absolute privacy.
Note: All security tools and hardware-modified devices discussed are intended for lawful use in authorized security research, corporate compliance, and personal privacy protection only.
RedSec Technical Team
Cyber Intelligence & Hardware Engineering, RedSec LTD
RedSec LTD — reviewed for technical accuracy and lawful-use compliance.
Sources & References
- 01USENIX
Discuss Your Requirements
Speak with our intelligence team about hardware-modified spy phones and authorized surveillance capabilities.
Request a ConsultationRelated Intelligence
The Evolution of Mobile Surveillance and Encrypted Communications Security
An expert analysis of the 2025 mobile threat landscape, focusing on zero-click exploits, state-sponsored malware, and the reality of encrypted communications security.
Spyware AnalysisThe Escalating Threat of Stalkerware and Consumer Surveillanceware
Stalkerware and consumer surveillanceware are reaching pandemic levels. We analyze the latest data breaches, security risks, and the rise of mobile malware.