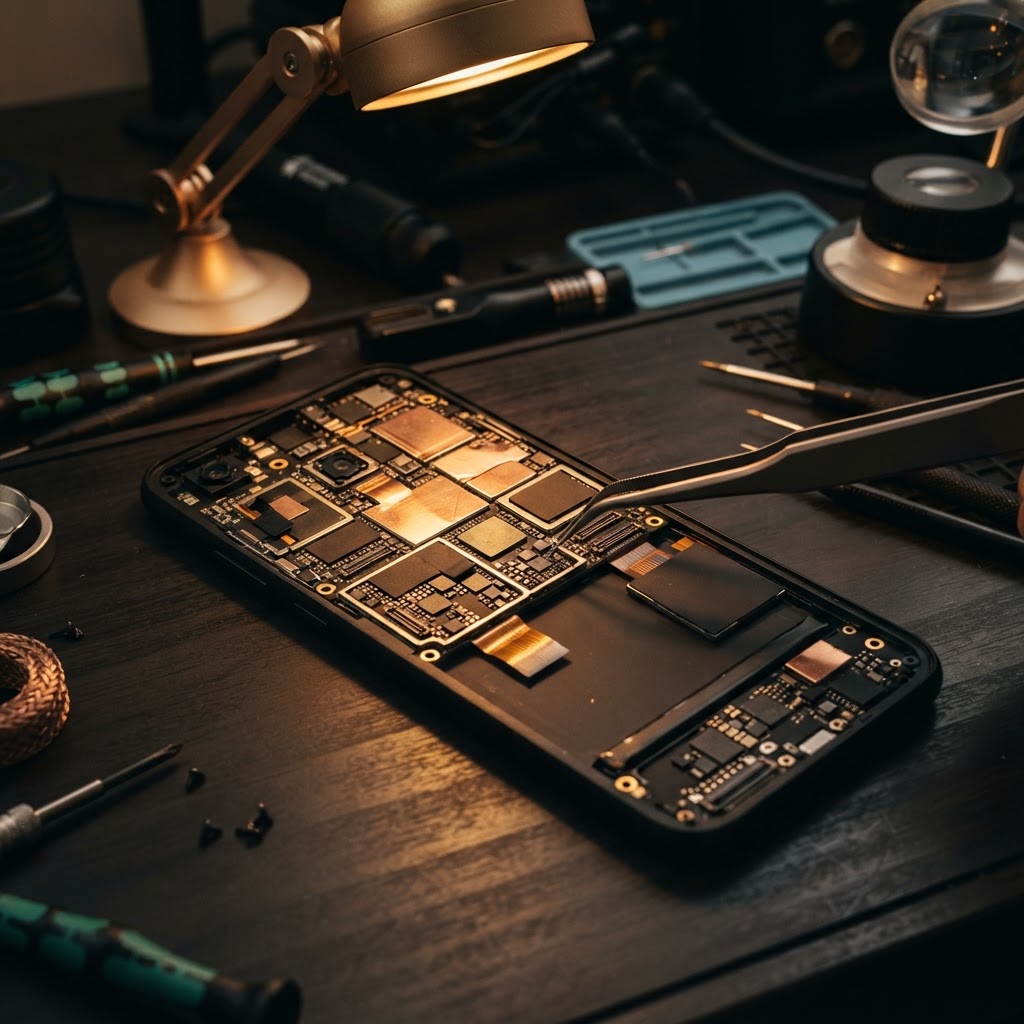
Silicon-Level Insecurity: Moving Past Software Exploits
Hardware surveillance represents the direct interception, tampering, or extraction of data at the component level, bypassing high-level operating system safeguards, application layers, and runtime memory protections. Historically, corporate and high-risk operators relied heavily on software mitigations to guard against cellphone spyware and advanced mobile malware. However, the operational battleground has shifted from the software layer straight into the device’s physical silicon architecture.
Modern smartphones operate as complex Systems-on-Chip (SoC) incorporating digital signal processors (DSPs), baseband modems, graphics units, and dedicated cryptographic enclaves. When vulnerabilities strike these low-level controllers, security boundaries disintegrate. As documented by recent disclosures surrounding active zero-day vulnerabilities in flagship Android chipsets—jointly tracked by vendors such as Qualcomm and Google (Computer Weekly)—threat actors leverage deep chipset-level flaws to establish persistence that operating system updates and standard anti-malware scanners cannot detect or purge.
At this tier, physical memory can be mapped, radio modems can be silently hijacked, and hardware registers can be read directly. This circumvents standard permissions entirely, rendering operating-system-level app restrictions ineffective against targeted, state-sponsored attacks.
The Architecture of Hardware-Modified Phones
To counter pervasive mobile surveillance, zero-click payloads, and continuous over-the-air baseband vulnerabilities, high-security operators are deploying hardware-modified phones. These devices are physically re-engineered to systematically eliminate analog attack vectors and radio frequency leak points that standard software cannot reliably disable.
Key architectural modifications include:
- Physical Sensor Severing: Complete desoldering and physical extraction of internal microphones, front/rear cameras, and ambient sensors. When an adversary deploys a Pegasus spyware alternative capable of turning on microphones silently, the exploit meets dead physical circuits and returns zero acoustic or optical signal.
- Baseband Isolation and External Interfaces: Baseband modems run proprietary, closed-source real-time operating systems (RTOS) that communicate directly with cellular towers. Hardware alterations decouple these modules, forcing data transmissions strictly over external, encrypted dongles or physically isolating the baseband power rails when offline.
- Hardware Disconnection Switches: Physical, analog micro-switches added to the device casing that mechanically disconnect the power delivery to Wi-Fi, Bluetooth, and GPS chips. Because operating systems can misreport "Airplane Mode" while leaving background radio frequency chips active, physical break-circuits guarantee true radio silence.
- Audited External Peripherals: Requiring external, hardware-toggled input/output devices (such as wired, switchable push-to-talk microphones) ensures that sensitive corporate conversations remain insulated even if the underlying operating system kernel suffers an unpatched zero-click attack.
Neutralizing Baseband Interception and Cellular Vectors
Every mobile device connects to carrier infrastructure through complex radio protocol stacks (such as 4G LTE and 5G non-standalone/standalone specifications). Cellular interception tools, including International Mobile Subscriber Identity (IMSI) catchers, rogue base stations, and airborne transceivers like "Dirtbox" systems, actively spoof legitimate cellular towers to harvest mobile metadata and force downgrades to insecure protocol states.
When a device is forced onto a hostile carrier channel, baseband vulnerabilities can grant threat actors remote code execution (RCE) prior to any end-to-end encryption software being engaged. By utilizing hardware-level modifications alongside specialized operating system distributions, security teams enforce strict radio frequency shielding and isolate baseband processors from application memory.
These measures preserve the integrity of encrypted communications. Software encryption running atop an exploited baseband processor risks memory-dump exfiltration or side-channel snooping; hardware-isolated architectures ensure that cryptographic keys, voice packets, and transit credentials are kept entirely quarantined within isolated hardware modules.
Implications for Mobile Forensics and C2 Operational Security
From the perspective of mobile forensics and operational command and control (C2), hardware surveillance fundamentally alters the evidentiary and defensive landscape. Forensic analysts conducting physical extractions on target devices typically rely on Joint Test Action Group (JTAG) interfaces, In-System Programming (ISP) breakouts, or USB diagnostics modes to dump flash memory.
Hardware-hardened devices prevent physical extraction by fusing, epoxy-potting, or physically destroying diagnostic test pads on the motherboard. When coupled with full-disk hardware encryption managed by zero-knowledge secure elements, forensic extraction tools cannot retrieve private keys through physical probing or side-channel voltage analysis.
Simultaneously, enterprise risk managers who oversee corporate devices through a secure C2 dashboard require definitive cryptographic attestation to confirm that a handset has not been physically interdicted or modified during transit. When rogue hardware components or modified silicon are inserted into the supply chain, high-assurance firmware attestation triggers tamper-evident lockout routines, preventing the compromised unit from authenticating to private communications infrastructure.
Key Takeaway
Software-level protection is no longer sufficient against nation-state surveillance; safeguarding critical corporate and investigative operations requires physical-layer isolation, hardware-modified phones, and zero-trust silicon architecture to effectively neutralize zero-click and hardware surveillance vectors.
Notice: The evaluation and deployment of hardware-modified technologies and forensic-resistant protocols must comply with relevant telecommunications laws and corporate governance frameworks.
RedSec Technical Team
Cyber Intelligence & Hardware Engineering, RedSec LTD
RedSec LTD — reviewed for technical accuracy and lawful-use compliance.
Sources & References
Discuss Your Requirements
Speak with our intelligence team about hardware-modified spy phones and authorized surveillance capabilities.
Request a ConsultationRelated Intelligence
The Illusion of Privacy: How Spyware Bypasses Encrypted Messaging Apps
Encrypted messaging apps like Signal and WhatsApp are under siege. Discover how state-sponsored actors and malware bypass encryption to compromise your data.
Threat IntelligenceThe Evolution of Consumer Surveillanceware: New Threats to Mobile Privacy
Analyze the latest trends in consumer surveillanceware. Learn how modern mobile malware and zero-click exploits are reshaping the landscape of mobile security.