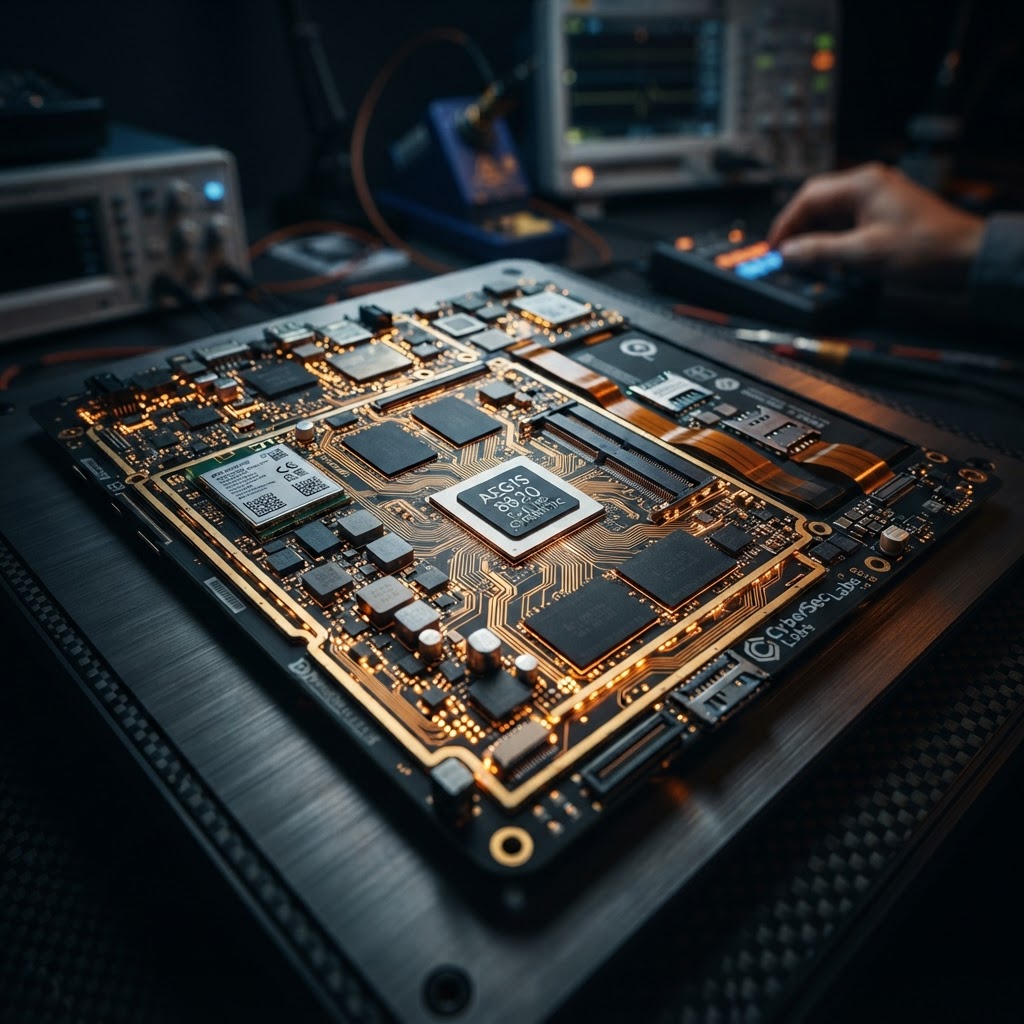
The Escalation of Hardware-Level Surveillance
In the current threat landscape, the security of mobile devices is no longer defined solely by software patches or operating system hardening. Recent intelligence reports, including the June 2026 disclosure by Russia’s Federal Security Service (FSB), highlight a shift toward sophisticated, persistent threats that target the very foundation of mobile hardware. Hardware-level surveillance refers to the integration of malicious code or physical modifications directly into the device’s firmware, baseband, or hardware components, allowing attackers to bypass standard security protocols. Unlike traditional mobile malware that resides in the application layer, these threats operate beneath the OS, making them nearly invisible to standard mobile forensics tools.
For professionals relying on encrypted communications, this evolution represents a critical failure point. When an adversary gains control at the hardware level, they can intercept calls, activate microphones, and exfiltrate data before encryption even occurs. This is the ultimate goal of advanced persistent threats (APTs) seeking to neutralize the privacy guarantees of hardware-modified phones.
Beyond Software: The Mechanics of Baseband and Firmware Exploitation
Modern cellphone spyware has moved beyond simple malicious apps. Today’s sophisticated campaigns utilize zero-click exploits—attacks that require no user interaction—to gain root-level access to the device’s baseband processor. The baseband is the subsystem responsible for all cellular radio communications. By compromising this component, an attacker can facilitate cellular interception without the user ever knowing their device has been tampered with.
This level of access allows for the deployment of persistent backdoors that survive factory resets. For organizations managing high-stakes communications, relying on consumer-grade hardware is increasingly untenable. The risk is not just in the software, but in the supply chain and the integrity of the hardware itself. When a device is compromised at the firmware level, the C2 dashboard used by the attacker can maintain a persistent connection, effectively turning the phone into a permanent listening device.
Defending Against Invisible Threats
Detecting hardware-modified phones requires a shift in strategy. Traditional antivirus solutions are ineffective against threats that reside in the bootloader or the device’s hardware abstraction layer. Security professionals must now employ advanced mobile forensics techniques, such as physical memory dumping and side-channel analysis, to identify anomalies in device behavior.
For those seeking a Pegasus spyware alternative or a more secure communication posture, the focus must be on hardware integrity. This includes utilizing devices with verified boot chains, disabled hardware sensors, and hardened baseband firmware. In an era where state-sponsored actors are actively targeting the hardware layer, the only way to ensure privacy is to control the entire stack—from the silicon up to the encrypted application layer.
Key Takeaway
Hardware-level surveillance has rendered traditional software-based security insufficient; organizations must prioritize hardware integrity, utilize hardened devices, and assume that any standard mobile device is a potential target for deep-level interception.
All products and services discussed are intended for lawful use in authorized security testing and professional compliance environments only.
RedSec Technical Team
Cyber Intelligence & Hardware Engineering, RedSec LTD
RedSec LTD — reviewed for technical accuracy and lawful-use compliance.
Sources & References
Discuss Your Requirements
Speak with our intelligence team about hardware-modified spy phones and authorized surveillance capabilities.
Request a ConsultationRelated Intelligence
Pegasus Spyware Evolution: The Escalating Threat of Commercial Surveillance
Recent investigations reveal Pegasus spyware is expanding beyond government use to target private sector executives, highlighting critical mobile security risks.
Threat IntelligenceSignal and WhatsApp Under Siege: The New Reality of Mobile Surveillance
State-sponsored actors are bypassing end-to-end encryption via linked-device exploits. Learn how to protect your communications from advanced mobile surveillance.